Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Microsoft Teams Enhances Security by Removing EXIF Data

Microsoft Teams Enhances Security by Removing EXIF Data

Posted on April 2, 2026 By CWS

In a strategic effort to bolster corporate privacy and security, Microsoft has unveiled a notable update for its Teams application. As part of the planned feature enhancements in March 2026, Microsoft Teams will automatically eliminate EXIF metadata from all images shared within its platform, across both chats and channels.

This default privacy measure is designed to shield users from the inadvertent exposure of sensitive location and device information to colleagues, external partners, or potential cyber threats. By proactively removing this data, Microsoft aims to close a significant security gap in digital communications.

Understanding the Risks of EXIF Metadata

EXIF metadata comprises hidden details embedded within digital images. Each time a photo is taken, the file stores specific information such as GPS coordinates, the date and time of capture, the device model, and the operating system version. From a cybersecurity standpoint, this information is a valuable resource for Open Source Intelligence (OSINT) activities.

Photos shared by employees, even those appearing innocent, can inadvertently disclose critical information such as home addresses or real-time travel patterns. Cybercriminals often exploit this metadata to execute targeted social engineering attacks or to track individuals of interest. Recognizing these vulnerabilities, Microsoft has integrated EXIF data scrubbing as an unchangeable feature in Teams.

Default Security Measures in Teams

With this update, any image uploaded to a direct chat or a company-wide channel will have its GPS location and device details removed automatically before reaching the recipient. This automation eliminates the need for users to manually clean their photos, ensuring that sensitive data remains confidential.

By embedding this security measure at the platform level, Microsoft provides users with the assurance that they can share visual content without risking unintended data leaks. For those who require sharing original metadata, alternative methods such as OneDrive links are recommended.

Enhanced Web Security Requirements

In addition to EXIF data removal, Microsoft is implementing stricter security standards for Teams web users. By May 15, 2026, the platform will require the use of modern browsers compliant with ECMAScript 2022 (ES2022). This transition will phase out outdated browsers, addressing legacy security vulnerabilities and promoting a more secure browsing environment.

These updates are seen as a significant advancement towards secure-by-design principles within the corporate sector. While the automatic removal of EXIF data may seem like a minor adjustment, it effectively addresses a longstanding blind spot in corporate communications. As remote work continues to grow, such automated safeguards are vital in maintaining enterprise privacy and security.

In summary, Microsoft’s commitment to enhancing security through these updates reflects a proactive approach to mitigating potential risks in digital interactions, ultimately fostering a more secure and private communication environment for all users.
Cyber Security News Tags:corporate security, Cybersecurity, ECMAScript 2022, EXIF data removal, Metadata, Microsoft Teams, OSINT, Privacy, remote work, web security

Post navigation

Previous Post: Linx Security Secures $50M to Enhance Identity Governance
Next Post: Starbucks Faces Cyber Breach: 10GB Data Allegedly Stolen

Related Posts

Windows Agere Modem Driver 0-Day Vulnerabilities Actively Exploited To Escalate Privileges Windows Agere Modem Driver 0-Day Vulnerabilities Actively Exploited To Escalate Privileges Cyber Security News
New OAuth-Based Attack Let Hackers Bypass Microsoft Entra Authentication Flows to Steal Keys New OAuth-Based Attack Let Hackers Bypass Microsoft Entra Authentication Flows to Steal Keys Cyber Security News
GhostApproval Flaw in Popular AI Coding Tools Raises Security Concerns GhostApproval Flaw in Popular AI Coding Tools Raises Security Concerns Cyber Security News
RondoDoX Botnet Weaponizing a Critical React2Shell Vulnerability to Deploy Malware RondoDoX Botnet Weaponizing a Critical React2Shell Vulnerability to Deploy Malware Cyber Security News
New HybridPetya Weaponizing UEFI Vulnerability to Bypass Secure Boot on Outdated Systems New HybridPetya Weaponizing UEFI Vulnerability to Bypass Secure Boot on Outdated Systems Cyber Security News
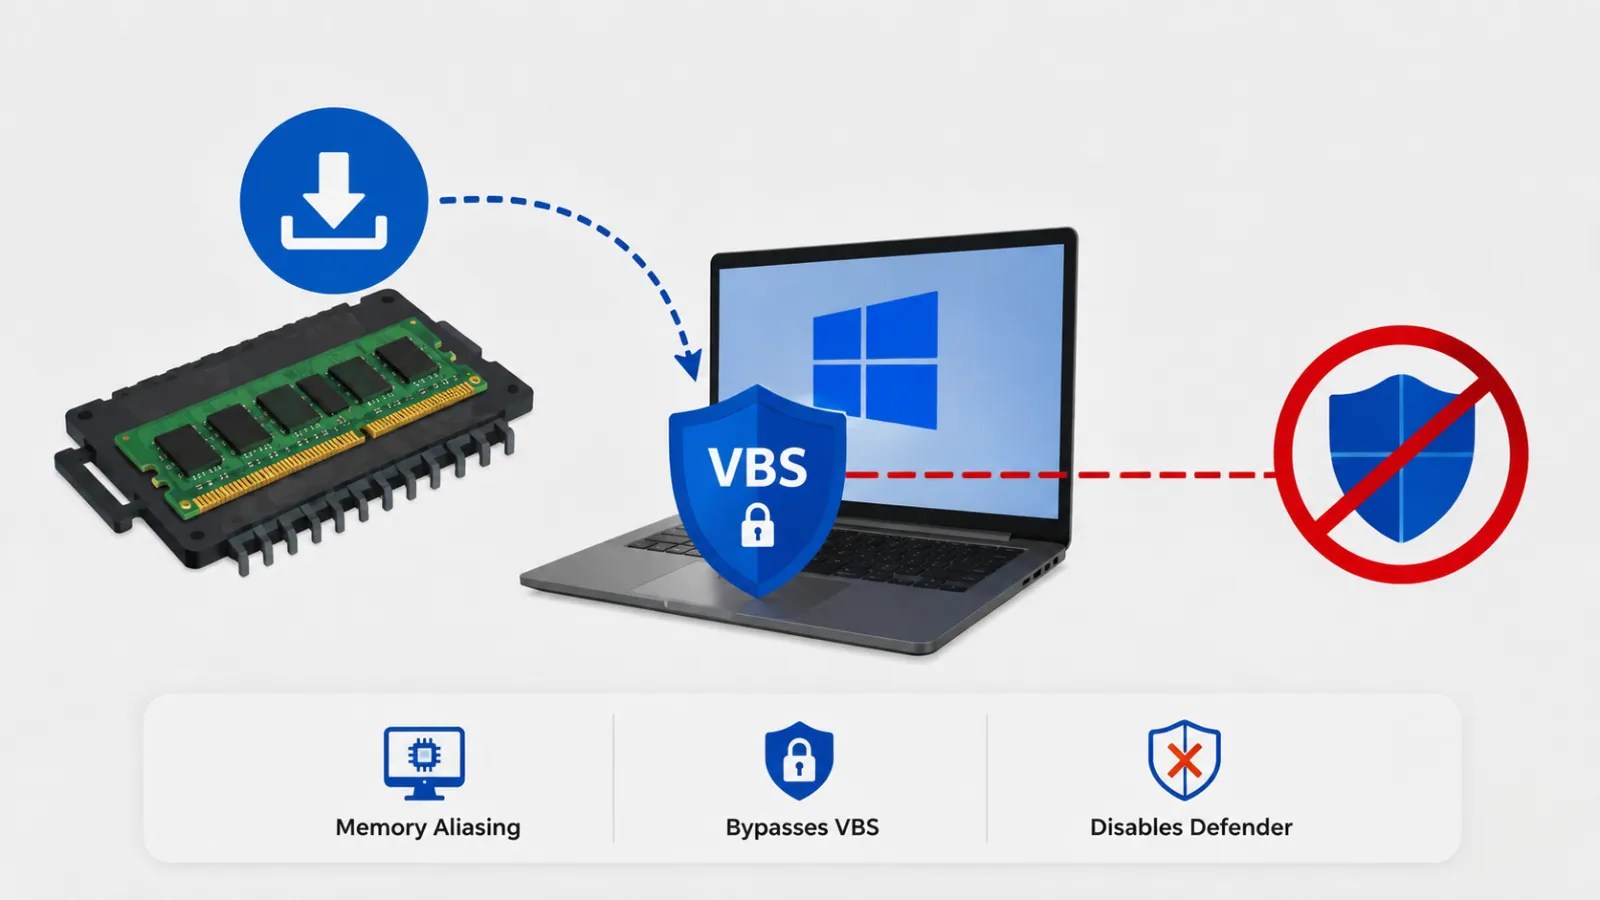
New RAM Exploit Bypasses Windows Security Barriers New RAM Exploit Bypasses Windows Security Barriers Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Internet Society Unveils Global Online Safety Resource
  • Bitget Uncovers Zero-Day Flaw in Major Crypto Heist
  • Citrix NetScaler Vulnerability Exploited by Threat Actors
  • Exploited PaperCut Server Breach Exposes Critical Flaws
  • AI Agents Expose 13,000 Screenshots from 300 Firms

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Internet Society Unveils Global Online Safety Resource
  • Bitget Uncovers Zero-Day Flaw in Major Crypto Heist
  • Citrix NetScaler Vulnerability Exploited by Threat Actors
  • Exploited PaperCut Server Breach Exposes Critical Flaws
  • AI Agents Expose 13,000 Screenshots from 300 Firms

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark