Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
NASA AIT-GUI Vulnerability Allows Unauthorized Commands

NASA AIT-GUI Vulnerability Allows Unauthorized Commands

Posted on August 20, 2026 By CWS

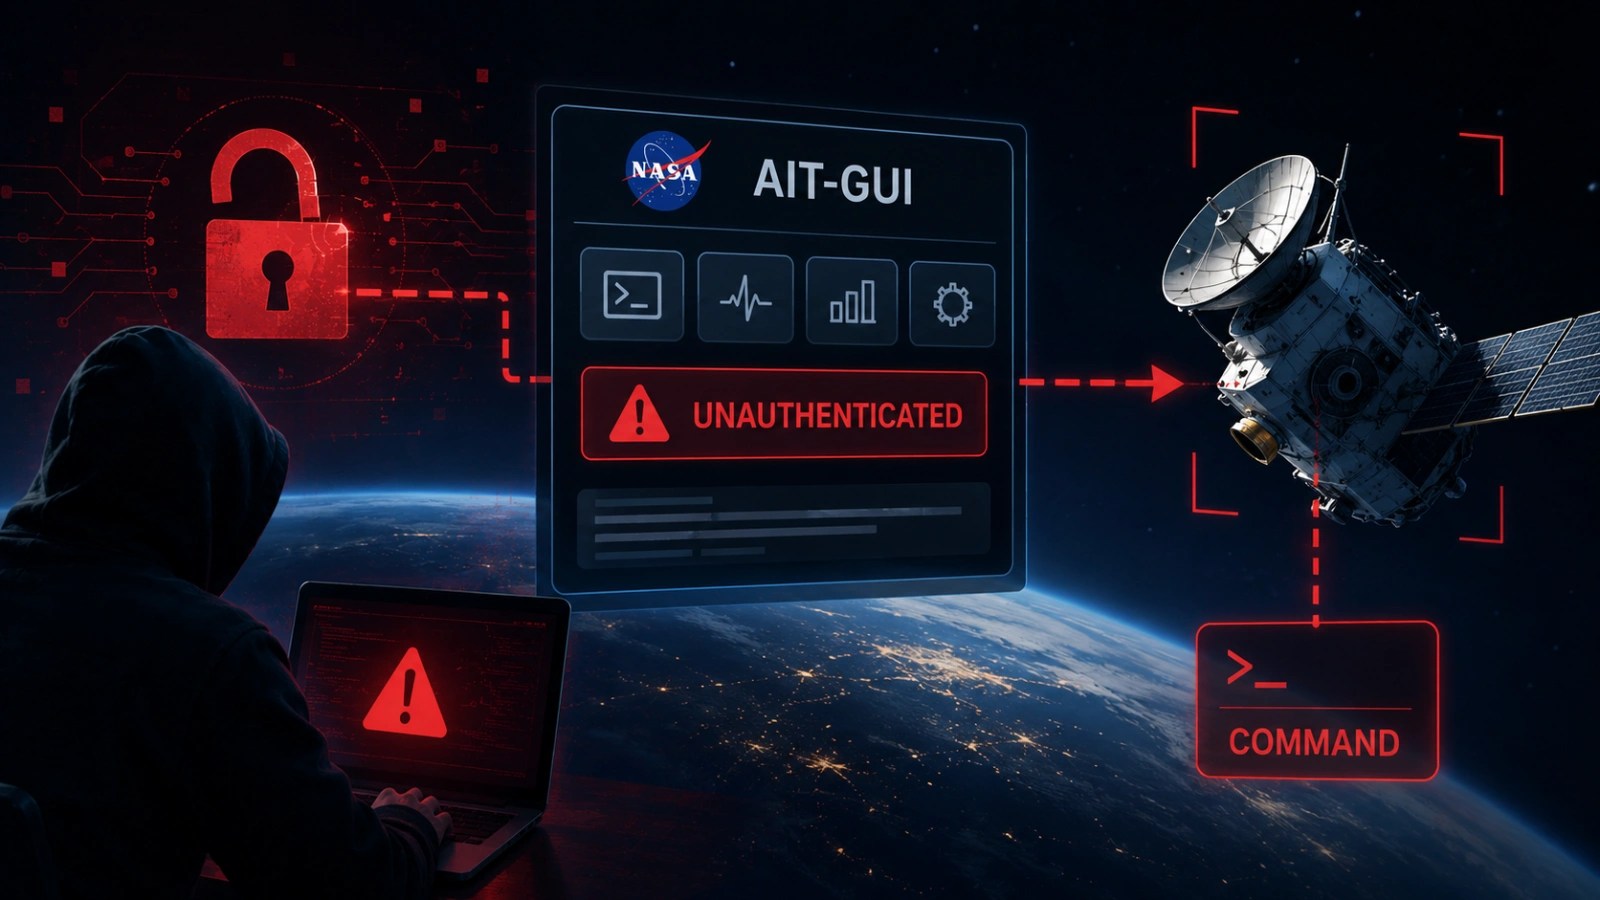
A significant security vulnerability in NASA’s AIT-GUI, used for controlling spacecraft and scientific instruments, has been identified. This flaw allows unauthorized individuals to issue commands without any need for authentication.

Security Flaw Details

Discovered by Yuval Elbar of Cycode, the flaw is rated at 9.4 on the CVSS v3.1 scale. It was addressed in version 2.5.2 of the AIT-GUI, released on August 12, 2026. This software is crucial as it functions as the interface for sending commands to spacecraft and processing telemetry data.

The root of the issue lies in the AIT-GUI web server’s configuration. It defaults to listening on all network interfaces, which exposes it to wider network access than intended. Furthermore, critical endpoints lack authentication and authorization measures, allowing potential attackers to execute commands without restrictions.

Associated Vulnerabilities

The problem is exacerbated by related vulnerabilities, such as CVE-2026-60112. This issue permits attackers to obtain a valid session without credentials, thereby executing arbitrary commands. This vulnerability, rated at 9.8, was disclosed prior to the main advisory.

Given the nature of the flaw, even systems protected from direct internet exposure are at risk if operators access malicious web pages. Browsers can send commands to the console without user interaction, making the vulnerability particularly dangerous.

Preventive Measures and Recommendations

NASA has released a patch with AIT-GUI version 2.5.2 and strongly advises users to upgrade immediately. It’s crucial to ensure that the console port is not accessible from untrusted networks. Additionally, reviewing command logs for anomalies is recommended to detect any prior unauthorized access.

For organizations maintaining these systems, enhancing security involves implementing authentication and authorization checks, securing the server configuration, and validating script paths to prevent unauthorized access. These measures are essential to protect against the operational risks posed by such vulnerabilities.

This incident highlights the importance of robust security practices in ground systems, emphasizing that these platforms are not immune to common web application vulnerabilities. Ensuring that these systems are secure is critical to prevent potential real-world consequences.
Cyber Security News Tags:AIT-GUI, Authentication, Authorization, CSRF, CVE-2026-60112, Cybersecurity, Cycode, ground systems, NASA, operational technology, security flaw, software vulnerability, Spacecraft

Post navigation

Previous Post: OpenAI Enhances AI Security with New Protocols
Next Post: Cybersecurity Threats Evolve: Key Developments

Related Posts

Sweet Security Brings Runtime-CNAPP Power to Windows Sweet Security Brings Runtime-CNAPP Power to Windows Cyber Security News
CISA Warns of Citrix Netscaler 0-day RCE Vulnerability Exploited in Attacks CISA Warns of Citrix Netscaler 0-day RCE Vulnerability Exploited in Attacks Cyber Security News
FortiWeb Authentication Bypass Vulnerability Exploited FortiWeb Authentication Bypass Vulnerability Exploited Cyber Security News
Windows 11 26H2 Enhances Backup Policy by Default Windows 11 26H2 Enhances Backup Policy by Default Cyber Security News
Atomic macOS Info-Stealer Upgraded With New Backdoor to Maintain Persistence Atomic macOS Info-Stealer Upgraded With New Backdoor to Maintain Persistence Cyber Security News
BreachLock Named a Leader in 2025 GigaOm Radar Report for Penetration Testing as a Service (PTaaS) for Third Consecutive Year BreachLock Named a Leader in 2025 GigaOm Radar Report for Penetration Testing as a Service (PTaaS) for Third Consecutive Year Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Trump Appoints Clayton to Lead Federal AI Task Force
  • South Korea Initiates Security Overhaul After Bank Data Breaches
  • China-Linked TA419 Targets U.S. AI Experts with Phishing
  • Key Arrest in ShinyHunters Case Aids FBI Investigation
  • Vercel Unveils KVM Zero-Day Flaw, Rewards Researcher $50K

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Trump Appoints Clayton to Lead Federal AI Task Force
  • South Korea Initiates Security Overhaul After Bank Data Breaches
  • China-Linked TA419 Targets U.S. AI Experts with Phishing
  • Key Arrest in ShinyHunters Case Aids FBI Investigation
  • Vercel Unveils KVM Zero-Day Flaw, Rewards Researcher $50K

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark