Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
FortiWeb Authentication Bypass Vulnerability Exploited

FortiWeb Authentication Bypass Vulnerability Exploited

Posted on November 14, 2025November 14, 2025 By CWS

Menace actors are actively exploiting a essential authentication bypass vulnerability in Fortinet’s FortiWeb internet software firewall (WAF) worldwide, prompting defenders to intensify vigilance.

Researchers at watchTowr Labs have responded by releasing a Detection Artefact Generator script, designed to assist organizations scan their environments for susceptible FortiWeb home equipment and mitigate dangers swiftly.​

The vulnerability, tracked as CVE-2025-52970, stems from improper parameter dealing with in FortiWeb, enabling unauthenticated distant attackers to log in as any current person by way of crafted requests.

With a CVSS rating of seven.7, it requires some personal data of the machine however poses extreme dangers, together with privilege escalation and potential distant code execution on affected techniques.

Fortinet patched the flaw in variations 8.0.2 and later, however in-the-wild assaults have surged since a partial proof-of-concept surfaced publicly in August 2025, focusing on uncovered FortiWeb situations indiscriminately.

Safety companies report dozens of compromises, underscoring the urgency for quick patching amid ongoing exploitation campaigns.​

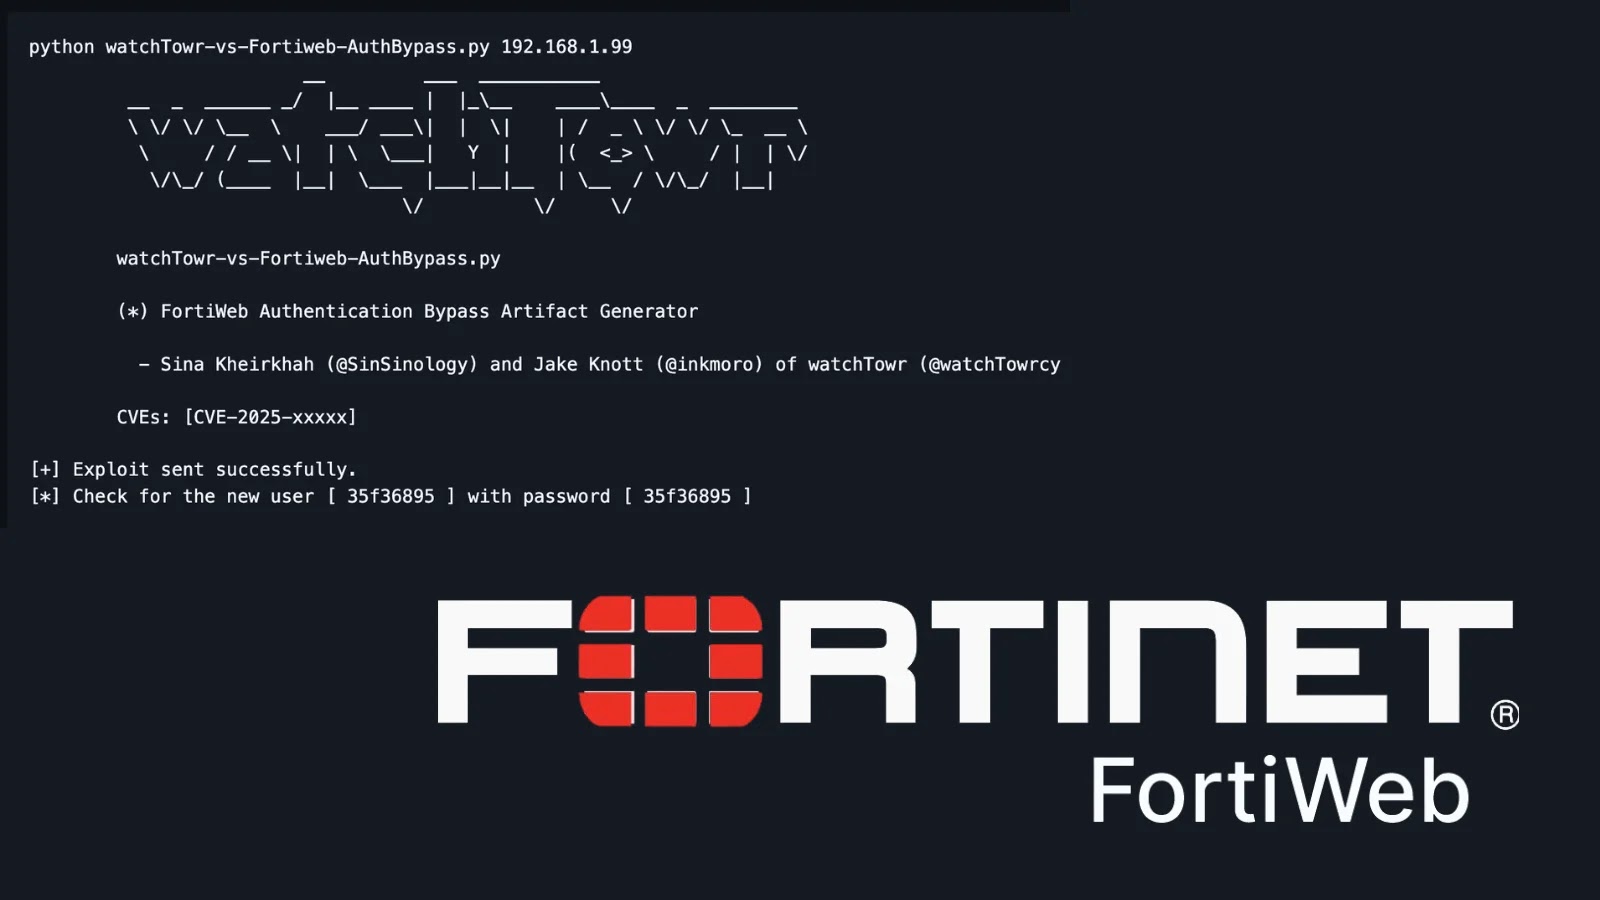
WatchTowr Labs’ open-source device, hosted on GitHub at watchTowr-vs-Fortiweb-AuthBypass, simplifies detection by simulating the bypass mechanism. The Python script generates a singular username and password (e.g., “35f36895”) and sends an exploit payload to the goal IP, comparable to python watchTowr-vs-Fortiweb-AuthBypass.py 192.168.1.99.

If profitable, it confirms vulnerability by creating a short lived person, alerting directors to remediate. Authored by Sina Kheirkhah (@SinSinology) and Jake Knott (@inkmoro), the script targets FortiWeb variations under 8.0.2, with specifics accessible by way of FortiGuard Labs PSIRT.​

Organizations ought to prioritize scanning internet-facing home equipment, making use of patches, and monitoring for anomalous logins. As provide chain assaults evolve, instruments like this empower proactive protection in a menace panorama the place WAFs sarcastically turn out to be entry factors.​

Observe us on Google Information, LinkedIn, and X for every day cybersecurity updates. Contact us to characteristic your tales.
Cyber Security News Tags:Authentication, Bypass, Exploited, FortiWeb, Vulnerability

Post navigation

Previous Post: Russian Hackers Create 4,300 Fake Travel Sites to Steal Hotel Guests’ Payment Data
Next Post: Critical Fortinet FortiWeb Vulnerability Exploited in the Wild to Create Admin Accounts

Related Posts

Chaos Ransomware Exploits Browsers as Secret Command Channels Chaos Ransomware Exploits Browsers as Secret Command Channels Cyber Security News
TOTOLINK X6000R Router Vulnerabilities Let Remote Attackers Execute Arbitrary Commands TOTOLINK X6000R Router Vulnerabilities Let Remote Attackers Execute Arbitrary Commands Cyber Security News
Cyber Attacks Targeting Education Sector Surges Following Back-to-School Season Cyber Attacks Targeting Education Sector Surges Following Back-to-School Season Cyber Security News
Aembit Expands Workload IAM to Microsoft Ecosystem, Enhancing Hybrid Security for Non-Human Identities Aembit Expands Workload IAM to Microsoft Ecosystem, Enhancing Hybrid Security for Non-Human Identities Cyber Security News
Broadcom Wi-Fi Flaw Exposes Millions of Routers to Attacks Broadcom Wi-Fi Flaw Exposes Millions of Routers to Attacks Cyber Security News
Jaguar Land Rover Confirms Employee Data Stolen in August Cyberattack Jaguar Land Rover Confirms Employee Data Stolen in August Cyberattack Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Identity Manager 10.0 LTS Enhances User Experience with AI
  • Enhanced Security with One Identity Active Roles 8.6
  • One Identity Releases Safeguard 9.0 for Enhanced PAM
  • CISA Alerts on Exploited Vulnerabilities in Key Software
  • Critical SAP Flaws Allow Unauthorized System Access

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Identity Manager 10.0 LTS Enhances User Experience with AI
  • Enhanced Security with One Identity Active Roles 8.6
  • One Identity Releases Safeguard 9.0 for Enhanced PAM
  • CISA Alerts on Exploited Vulnerabilities in Key Software
  • Critical SAP Flaws Allow Unauthorized System Access

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark