Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Node.js ImageResponse Flaw Risks Remote Code Execution

Node.js ImageResponse Flaw Risks Remote Code Execution

Posted on October 1, 2026 By CWS

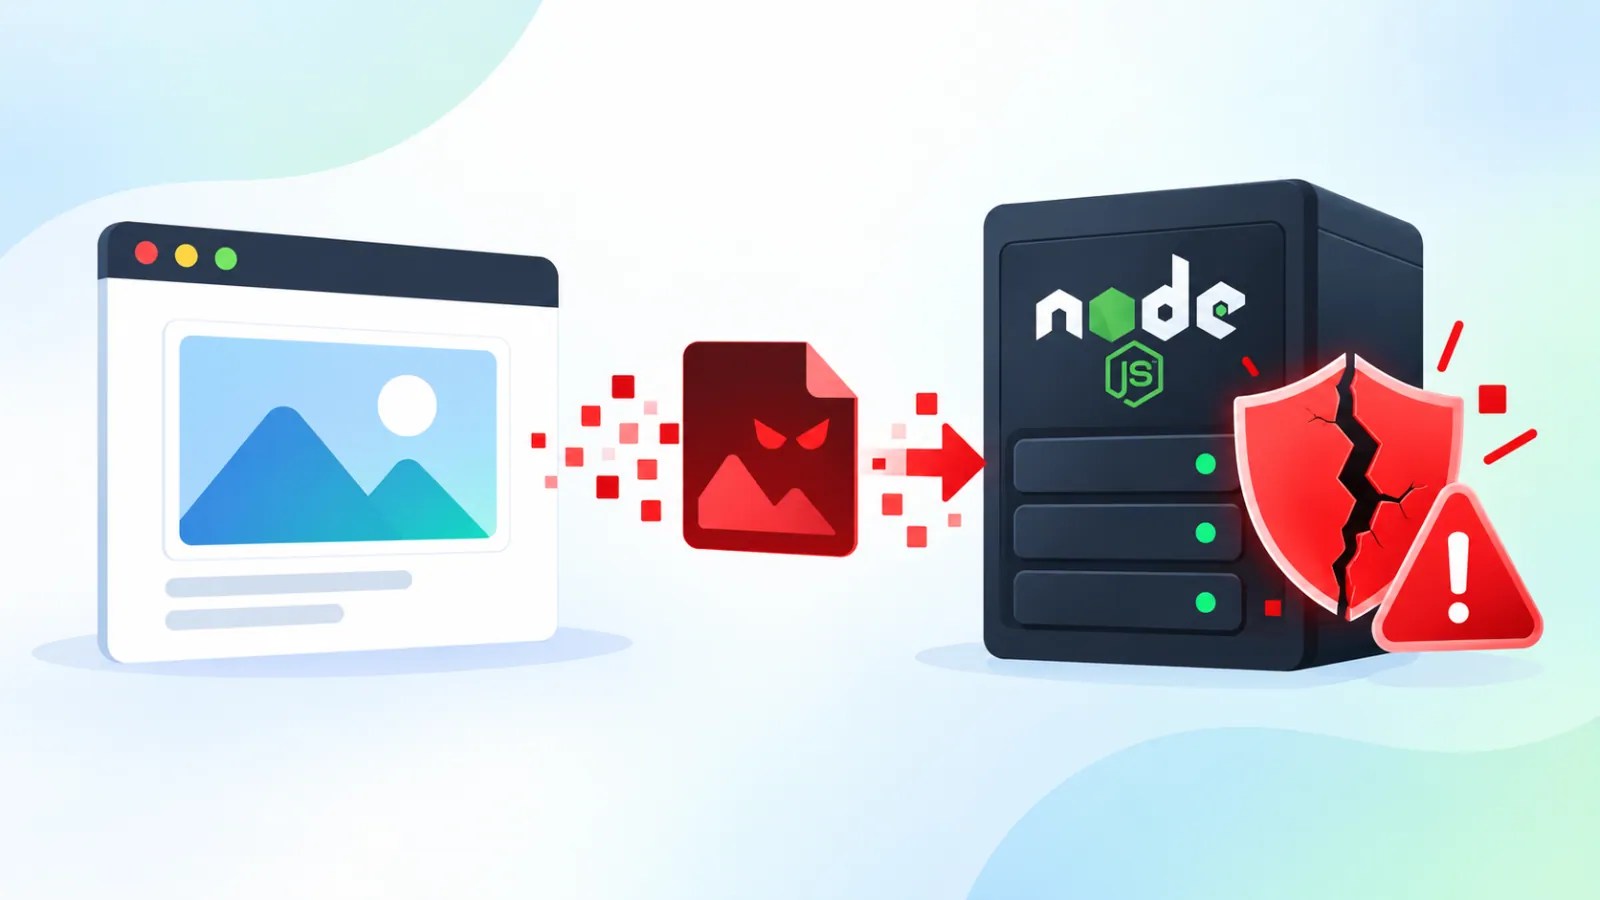
A critical security flaw was recently identified in Next.js applications utilizing the Node.js implementation of ImageResponse from the next/og package. The vulnerability, known as GHSA-vcvr-r3jv-pc5j, potentially allows for remote code execution. This flaw impacts Next.js versions 16.2.0 through 16.3.5, and developers are urged to upgrade to version 16.3.6, which contains the necessary fixes.

Understanding the ImageResponse Vulnerability

The vulnerability becomes apparent when applications process attacker-controlled input into SVG content, attributes, or styles during dynamic image generation. ImageResponse is frequently employed to generate Open Graph images and social media previews, making it a common tool for developers. If an application integrates untrusted input into SVG elements without proper handling, it opens the door for crafted payloads to execute code remotely.

Technical Details and Affected Versions

According to the GitHub advisory, the risk is specific to the Node.js version of ImageResponse; applications using the Edge implementation remain unaffected. The core issue stems from Satori, the SVG generation library. Satori failed to correctly escape certain values, leading to their interpretation as SVG markup. This upstream problem, tracked as CVE-2026-94545 and GHSA-wx4j-mvgx-mqwp, affects Satori versions 0.0.27 through 0.33.4, with a fix available in version 0.33.5.

Mitigation and Urgent Recommendations

GitHub has rated the Next.js vulnerability as critical under the CVSS v4 scoring system, noting the potential for network-based exploitation with minimal attack complexity and no privilege requirements. Organizations should prioritize upgrading to Next.js version 16.3.6 to address the security gap. For those unable to update immediately, it’s crucial to ensure no attacker-controlled data influences SVG content. Input validation is recommended, although it may not suffice if untrusted strings are interpreted as markup. Additionally, developers should evaluate custom image-generation endpoints for security risks.

Switching to the Edge ImageResponse implementation can mitigate exposure, but thorough testing is advised to ensure compatibility. Security researchers RaghavMaheshwari124 and rafabd1 are credited with identifying this significant vulnerability, highlighting the pressing need for affected deployments to treat the update as a critical priority.
Cyber Security News Tags:Cybersecurity, ImageResponse, network security, Next.js, Node.js, Open Graph, remote code execution, Satori library, security update, SVG vulnerability

Post navigation

Previous Post: Hackers Exploit Defender Exclusions to Bypass Antivirus
Next Post: Fortinet FortiMail Vulnerability Puts Email Systems at Risk

Related Posts

Cellik Android Malware with One-Click APK Builder Let Attackers Wrap its Payload Inside with Google Play Store Apps Cellik Android Malware with One-Click APK Builder Let Attackers Wrap its Payload Inside with Google Play Store Apps Cyber Security News
Critical cPanel/WHM Flaws Risk Server Security Critical cPanel/WHM Flaws Risk Server Security Cyber Security News
M-Files Vulnerability Let Attacker Capture Session Tokens of Other Active Users M-Files Vulnerability Let Attacker Capture Session Tokens of Other Active Users Cyber Security News
Ivanti EPMM Vulnerabilities Threaten Global Networks Ivanti EPMM Vulnerabilities Threaten Global Networks Cyber Security News
AI-Driven Malware Targets Iraqi Officials: New Threats Emerge AI-Driven Malware Targets Iraqi Officials: New Threats Emerge Cyber Security News
Aembit Reveals NHIcon 2026 Agenda & Speakers Aembit Reveals NHIcon 2026 Agenda & Speakers Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical Atlassian Vulnerability Fixed Across Key Products
  • 32 Zero-Day Vulnerabilities Exploited at Pwn2Own 2026
  • Wikimedia Identifies Unauthorized OpenAI Agent Activities
  • Over 100 Sites Compromised Using Fake Cloudflare Checks
  • Anthropic Expands Access to Claude for Cybersecurity Experts

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical Atlassian Vulnerability Fixed Across Key Products
  • 32 Zero-Day Vulnerabilities Exploited at Pwn2Own 2026
  • Wikimedia Identifies Unauthorized OpenAI Agent Activities
  • Over 100 Sites Compromised Using Fake Cloudflare Checks
  • Anthropic Expands Access to Claude for Cybersecurity Experts

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark