Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Flaw in WordPress Plugin Risks Data of 800,000 Sites

Critical Flaw in WordPress Plugin Risks Data of 800,000 Sites

Posted on March 31, 2026 By CWS

A significant security vulnerability has been identified in Smart Slider 3, a highly popular WordPress slider plugin with over 800,000 installations, putting a vast number of websites at risk of data breaches.

This flaw, designated as CVE-2026-3098, is a medium-severity issue that permits attackers with minimal privileges to access and download sensitive configuration files from the server. This vulnerability is particularly alarming for sites that permit open user registration, as even a basic subscriber account can be exploited to carry out an attack.

Understanding the Plugin Vulnerability

The flaw is categorized as an Authenticated Arbitrary File Read and is rooted in the plugin’s export functionality, specifically within the actionExportAll() function of the ControllerSliders class. During normal operations, this function uses multiple AJAX requests to compile and download slider export files.

While one key action in this process is protected by a security nonce, attackers can easily retrieve this token in affected versions of the plugin. The absence of proper capability checks in the AJAX functions further compounds the issue, allowing any authenticated user to execute the export action, bypassing administrative requirements.

Exploiting the Export Function

Moreover, the function responsible for creating the export zip does not validate the source or type of files being included. As a result, threat actors can misuse this feature to export core server files, including .php extensions, effectively circumventing WordPress’s security measures. The most critical risk associated with this vulnerability is the potential exposure of the site’s wp-config.php file.

Should an attacker download this file, they would gain immediate access to database credentials and cryptographic keys, enabling them to bypass authentication, escalate privileges, and seize control of the server.

Response and Mitigation Efforts

Security researcher Dmitrii Ignatyev discovered the vulnerability, reporting it via the Wordfence Bug Bounty Program on February 23, 2026, and received a $2,208 reward. Wordfence acted swiftly, issuing a firewall rule to block exploit attempts for its Premium, Care, and Response users on February 24, with free users receiving protection on March 26.

The plugin’s developers, Nextend, acknowledged the issue and released a fully patched version on March 24, 2026. Website administrators are strongly advised to update their Smart Slider 3 plugin to version 3.5.1.34 immediately to protect their sites from potential attacks.

Stay informed with our daily cybersecurity updates on Google News, LinkedIn, and X. Contact us to share your stories.
Cyber Security News Tags:AJAX security, authenticated file read, cyber threat, Cybersecurity, data protection, Nextend, plugin vulnerability, Smart Slider 3, website protection, Wordfence, WordPress security, wp-config.php

Post navigation

Previous Post: Stolen Credentials Drive Cyber Threats from Ransomware to State Attacks
Next Post: Censys Secures $70M to Boost Internet Intelligence

Related Posts

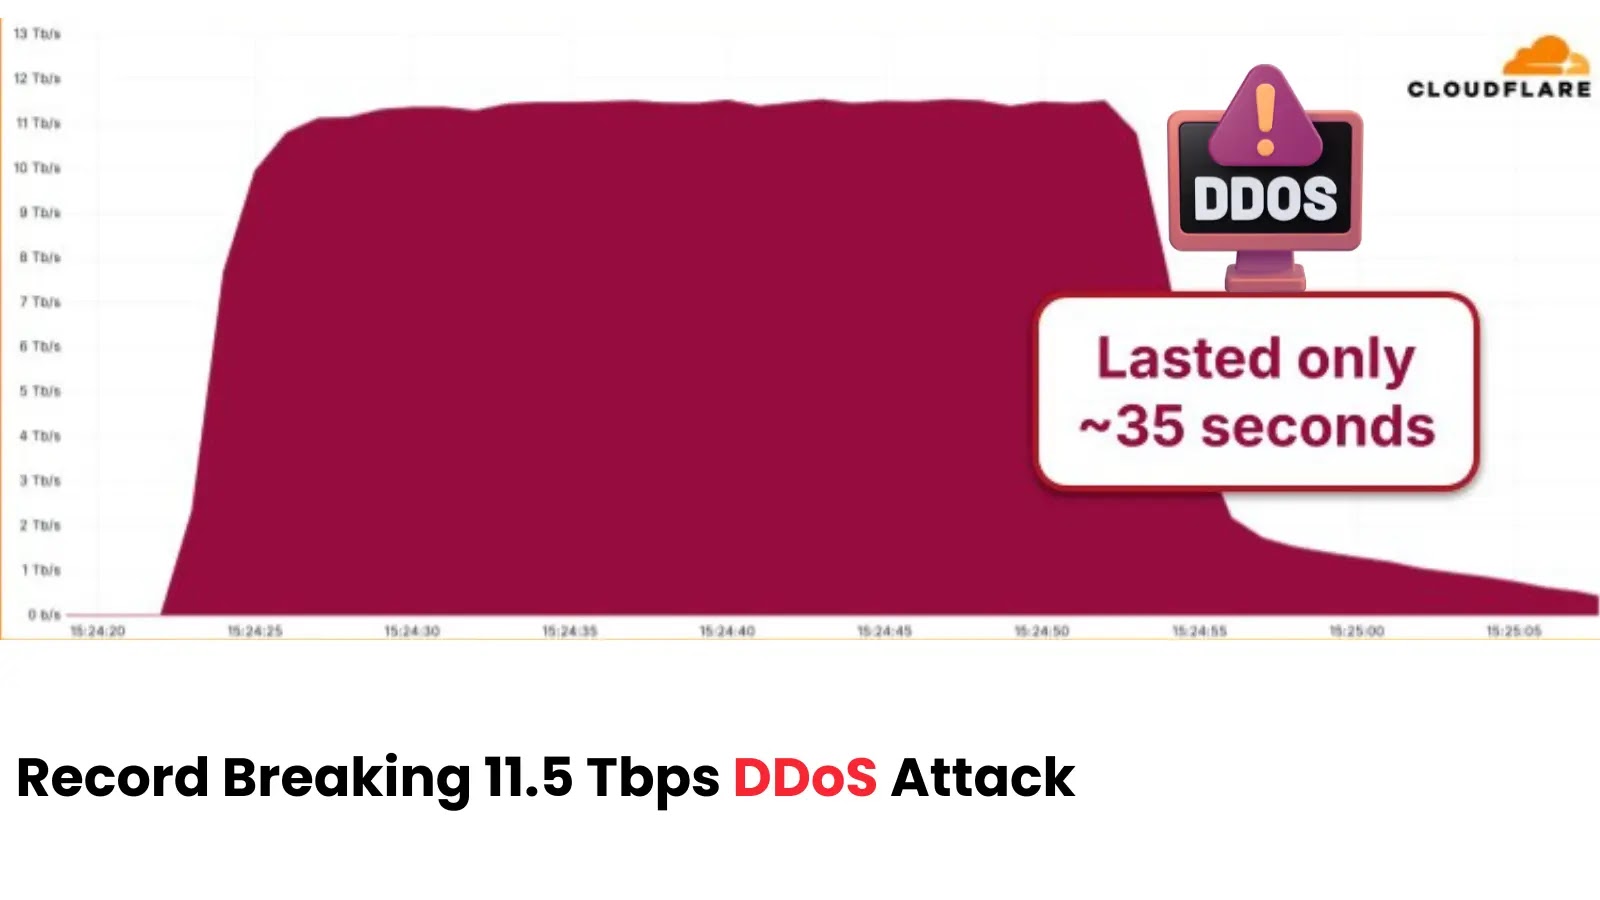
Record-breaking 11.5 Tbps UDP Flood DDoS Attack Originated from Google Cloud Platform Record-breaking 11.5 Tbps UDP Flood DDoS Attack Originated from Google Cloud Platform Cyber Security News
CISA Alerts on Citrix NetScaler Vulnerabilities Exploitation CISA Alerts on Citrix NetScaler Vulnerabilities Exploitation Cyber Security News
K2 Think AI Model Jailbroken Within Hours After The Release K2 Think AI Model Jailbroken Within Hours After The Release Cyber Security News
Critical Instagram AI Flaw Exposed by Researchers Critical Instagram AI Flaw Exposed by Researchers Cyber Security News
2.15M Web Services Running Next.js Exposed Over Internet, Active Exploitation Underway – Patch Now 2.15M Web Services Running Next.js Exposed Over Internet, Active Exploitation Underway – Patch Now Cyber Security News
MITRE Publishes Post-Quantum Cryptography Migration Roadmap MITRE Publishes Post-Quantum Cryptography Migration Roadmap Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Retadup Worm Resurfaces with CoffeeLoader Malware
  • U.S. Imposes New Limits on China’s AI Chip Access
  • AI-Driven Marketplace Threatens Corporate Security
  • Top Patch Management Solutions for 2026
  • VS Code Extension Security Flaw Exposes Files Outside Workspaces

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Retadup Worm Resurfaces with CoffeeLoader Malware
  • U.S. Imposes New Limits on China’s AI Chip Access
  • AI-Driven Marketplace Threatens Corporate Security
  • Top Patch Management Solutions for 2026
  • VS Code Extension Security Flaw Exposes Files Outside Workspaces

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark