Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Hackers Exploit Ninja Forms Vulnerability on WordPress

Hackers Exploit Ninja Forms Vulnerability on WordPress

Posted on April 8, 2026 By CWS

A critical vulnerability affecting the File Uploads addon within the Ninja Forms WordPress plugin has been identified, potentially allowing cybercriminals to seize control of susceptible websites. Cybersecurity firm Defiant has issued a warning regarding this significant threat.

Extent of the Vulnerability

The affected addon is reportedly utilized by approximately 50,000 websites, with Defiant observing numerous exploitation attempts. The flaw, designated as CVE-2026-0740 and assigned a CVSS score of 9.8, is characterized as an unauthenticated arbitrary file upload vulnerability.

This security issue arises from inadequate file type validation, which is essential for the functionality designed to manage file uploads within the Ninja Forms plugin. Specifically, the flaw is located in the process that saves uploaded files to the designated uploads folder.

Technical Details and Risks

The vulnerability stems from insufficient verification of the destination filename before files are moved to the uploads directory, enabling the upload of files with a .php extension. According to Defiant, the absence of filename sanitization facilitates path traversal, potentially allowing files to be moved to the webroot directory.

This flaw permits unauthenticated attackers to upload malicious PHP code to the server of a vulnerable website, subsequently enabling them to execute remote code execution (RCE). Through this exploit, attackers can deploy web shells and potentially gain comprehensive control over the affected website.

Response and Recommendations

The vulnerability, discovered and reported by security researcher Sélim Lanouar through the Wordfence bug bounty program in January, earned a reward of $2,145. Users of the Ninja Forms – File Uploads plugin are strongly urged to update to version 3.3.27 promptly, as all preceding versions are susceptible to this issue.

In light of this vulnerability, it is crucial for website administrators to act swiftly in upgrading their plugins to mitigate potential security risks. The update aims to rectify the identified flaw and bolster the overall security posture of websites using the Ninja Forms plugin.

Related topics of interest include vulnerabilities in the Flowise and King Addons plugins, and the GrafanaGhost exploit, which also pose significant security threats to WordPress sites.

Security Week News Tags:CVE-2026-0740, Cybersecurity, Defiant, file upload exploit, Ninja Forms, plugin vulnerability, remote code execution, Vulnerability, web security, WordPress security

Post navigation

Previous Post: FBI Halts Russian Cyberattack on Routers
Next Post: Windows 11 Update Causes Start Menu Issues, Fix Deployed

Related Posts

Guardz Banks M Series B for All-in-One SMB Security Guardz Banks $56M Series B for All-in-One SMB Security Security Week News
re:Invent 2025: AWS and Security Vendors Unveil New Products and Capabilities  re:Invent 2025: AWS and Security Vendors Unveil New Products and Capabilities  Security Week News
HyperBunker Raises Seed Funding to Launch Next-Generation Anti-Ransomware Device HyperBunker Raises Seed Funding to Launch Next-Generation Anti-Ransomware Device Security Week News
Critical Flowise Vulnerability Exploit Code Released Critical Flowise Vulnerability Exploit Code Released Security Week News
Key Cybersecurity Updates: Microsoft Patches, Dropbox Breach Key Cybersecurity Updates: Microsoft Patches, Dropbox Breach Security Week News
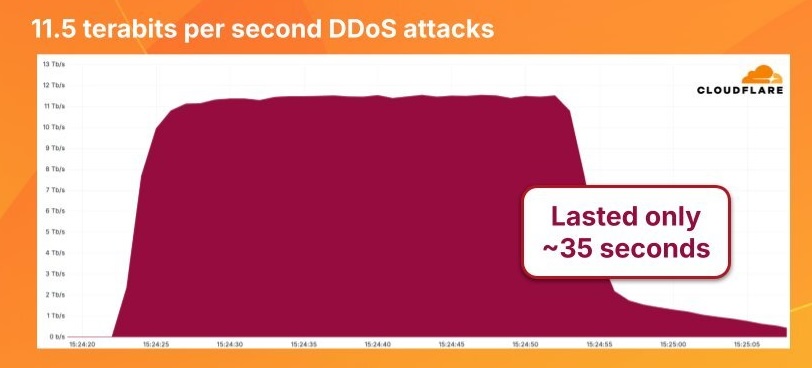
Cloudflare Blocks Record-Breaking 11.5 Tbps DDoS Attack Cloudflare Blocks Record-Breaking 11.5 Tbps DDoS Attack Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • AppViewX Enhances AI Security with New Tools
  • Cyberattack Exposes Data of Over 1 Million in Arizona Courts
  • Criminal IP Unveils AITEM: Revolutionizing Cybersecurity
  • Iranian Hackers Exploit Fake Coding Test to Infiltrate Iraqi Systems
  • Aembit Enhances Security for AI Agents in Enterprises

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • AppViewX Enhances AI Security with New Tools
  • Cyberattack Exposes Data of Over 1 Million in Arizona Courts
  • Criminal IP Unveils AITEM: Revolutionizing Cybersecurity
  • Iranian Hackers Exploit Fake Coding Test to Infiltrate Iraqi Systems
  • Aembit Enhances Security for AI Agents in Enterprises

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark