Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Hackers Target VMware vCenter Flaw for Remote Access

Hackers Target VMware vCenter Flaw for Remote Access

Posted on August 12, 2026 By CWS

Cybersecurity experts have identified active exploitation of a critical vulnerability in Broadcom’s VMware vCenter, posing significant risks to affected systems. The flaw, tracked as CVE-2026-59310, allows attackers with network access to execute arbitrary code, with a CVSS score of 9.8 highlighting its severity.

Exploitation Details and Attack Methodology

The German cybersecurity firm QUIRSO discovered evidence of exploitation during an incident response, revealing that attackers are utilizing a path traversal technique to deploy malicious cron jobs. These jobs harness the reverse_ssh tool to maintain a foothold on compromised systems. This tool facilitates SSH connections to infrastructure controlled by threat actors, enabling persistent access.

QUIRSO’s analysis indicates that compromised systems began communicating with attackers’ domains soon after Broadcom’s public disclosure of the flaw. The breach has affected 361 unique IP addresses across 47 countries, with Germany, the U.S., Turkey, Iran, and France being the most impacted.

Potential Attribution and Historical Context

While the identity of the attackers remains unknown, speculation points to an advanced persistent threat (APT) group. Historically, VMware appliances have been attractive targets for Chinese threat actors like UNC5174, who have conducted espionage by exploiting vulnerabilities in VMware products.

In a related instance, SentinelOne previously uncovered a threat cluster called PurpleHaze, which targeted South Asian entities using a backdoor named GoReShell. This backdoor also employed reverse_ssh to establish connections to attacker-controlled hosts, underscoring the persistent interest in VMware vulnerabilities by various threat actors.

Ongoing Investigations and Security Implications

The cybersecurity community is on high alert following reports from Defused Cyber of increased scanning activity targeting VMware vCenter. This activity suggests potential exploitation of both CVE-2026-59310 and another related flaw, CVE-2026-59309.

Denis Szadkowski, COO of QUIRSO, emphasized that current evidence more strongly supports CVE-2026-59310 as the vector for successful intrusions, rather than mere exploitation attempts. The presence of reverse_ssh, while not necessarily indicative of malevolent intent, becomes a critical concern when paired with unauthorized installations or unexpected outbound connections.

As cybersecurity professionals continue their investigations, organizations using VMware vCenter are urged to apply patches promptly and monitor for signs of compromise. The situation serves as a reminder of the importance of timely updates and vigilance in the face of evolving cybersecurity threats.
The Hacker News Tags:APT, Broadcom, CVE-2026-59310, cyber attack, Cybersecurity, reverse SSH, threat intelligence, vCenter, VMware, Vulnerability

Post navigation

Previous Post: North Korean Hackers Exploit Fresh Windows Vulnerability
Next Post: LiteLLM Supply Chain Attack Affects Over 2,500 Organizations

Related Posts

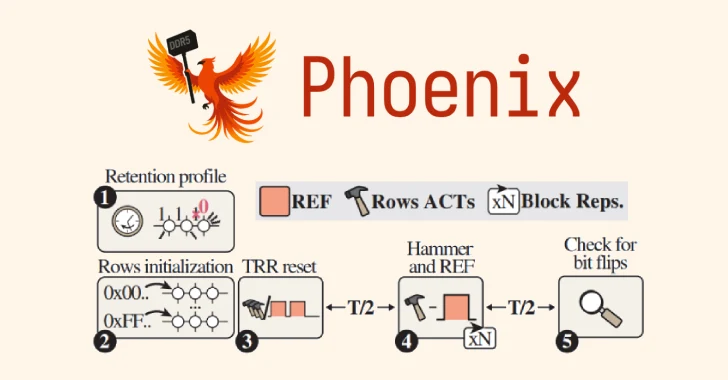
Phoenix RowHammer Attack Bypasses Advanced DDR5 Memory Protections in 109 Seconds Phoenix RowHammer Attack Bypasses Advanced DDR5 Memory Protections in 109 Seconds The Hacker News
Amazon Kiro Vulnerability Risks Data Exposure Amazon Kiro Vulnerability Risks Data Exposure The Hacker News
Hugging Face Diffusers Security Flaws Threaten AI Systems Hugging Face Diffusers Security Flaws Threaten AI Systems The Hacker News
Qilin Ransomware Adds “Call Lawyer” Feature to Pressure Victims for Larger Ransoms Qilin Ransomware Adds “Call Lawyer” Feature to Pressure Victims for Larger Ransoms The Hacker News
Critical Open VSX Registry Flaw Exposes Millions of Developers to Supply Chain Attacks Critical Open VSX Registry Flaw Exposes Millions of Developers to Supply Chain Attacks The Hacker News
Apache ActiveMQ Flaw Exploited to Deploy DripDropper Malware on Cloud Linux Systems Apache ActiveMQ Flaw Exploited to Deploy DripDropper Malware on Cloud Linux Systems The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical Nintendo Switch Flaw Allows Code Execution
  • Telegram Desktop Update Fixes Critical JavaScript Flaw
  • UK Introduces Passkeys for 23 Million GOV.UK Users
  • 3BB Network Breach: MeshCentral Backdoor Exploited
  • Massive Vite Server Vulnerability Exploited for Cloud Credential Theft

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical Nintendo Switch Flaw Allows Code Execution
  • Telegram Desktop Update Fixes Critical JavaScript Flaw
  • UK Introduces Passkeys for 23 Million GOV.UK Users
  • 3BB Network Breach: MeshCentral Backdoor Exploited
  • Massive Vite Server Vulnerability Exploited for Cloud Credential Theft

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark