Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Mastering Exposure Prioritization: Key Strategies Revealed

Mastering Exposure Prioritization: Key Strategies Revealed

Posted on November 3, 2026 By CWS

Organizations are grappling with an overwhelming number of vulnerabilities, yet breach risks remain stubbornly high. Many teams focus on exposures unlikely to be exploited, while high-risk vulnerabilities linger. According to Gartner’s report on exposure prioritization, less than 10% of vulnerabilities are exploited, but most are treated with urgency. Traditional reliance on CVSS scores fails to accurately predict exploitation risks or business impacts.

Rethinking Vulnerability Prioritization

Gartner forecasts that by 2028, businesses prioritizing exposures using threat intelligence, asset context, exploitability modeling, and security control validation will see a 70% reduction in breach likelihood, compared to those relying on CVSS-based prioritization. Understanding these elements and their integration is crucial for effective vulnerability management.

Previously, severity-based prioritization was effective in a static environment with limited vulnerabilities. However, today’s dynamic landscape, characterized by numerous vulnerabilities across cloud and other modalities, requires a fresh approach. The current focus on severity can lead to prioritization paralysis, consuming resources with minimal risk reduction.

The Four Pillars of Effective Exposure Management

Gartner’s framework consists of four pillars, each addressing a specific query about exposure. The true value of these elements unfolds when they are combined. Implementing all four significantly decreases exposure windows and reduces remediation fatigue.

Threat Intelligence

Threat intelligence provides insights into which exposures are actively exploited by adversaries. Often, attackers target moderately rated vulnerabilities due to ease of exploitation or prevalence. Speed is crucial; teams must quickly act on intelligence to mitigate threats before they materialize.

Asset Context and Business Criticality

A vulnerability’s risk elevates when it impacts assets that are critical to business operations or handle sensitive data. Without considering asset context, prioritization may overlook critical systems. Existing tools like CMDBs and cloud security platforms can provide necessary context, requiring integration and real-time updates.

Exploitability and Security Validation

Exploitability Modeling

Models like EPSS help estimate the likelihood of exploitation, complementing threat intelligence by identifying latent risks. However, these models offer a general perspective, and validation within specific environments is essential to determine actual exploitability.

Security Control Validation

Security control validation assesses how well current defenses protect against specific exposures. Sometimes, exposures that seem critical are well-protected by existing controls, whereas less obvious ones may pose greater risks. Validation ensures realistic risk assessment and efficient resource use.

The integration of these elements is where many organizations struggle. Often, intelligence, context, and modeling data are siloed. Picus Platform addresses this by unifying these aspects into a continuous loop of discovery, validation, prioritization, and mobilization, enhancing decision-making and reducing breach risks.

For organizations seeking to enhance their vulnerability management practices, understanding and applying these elements is crucial. A demo of the Picus Platform can demonstrate how validated prioritization transforms scanner findings into actionable insights.

The Hacker News Tags:adversarial exposure validation, asset context, breach risk reduction, continuous threat exposure management, CVE, Cybersecurity, exploitability modeling, exposure prioritization, Gartner report, penetration testing, Picus Platform, risk management, security control validation, threat intelligence, vulnerability management

Post navigation

Previous Post: Microsoft Unveils Key Insights Into System Vulnerabilities
Next Post: Node-RED Vulnerability Exploited by Hackers: Key Insights

Related Posts

WordPress Patch Fixes Critical Comment2Shell Vulnerability WordPress Patch Fixes Critical Comment2Shell Vulnerability The Hacker News
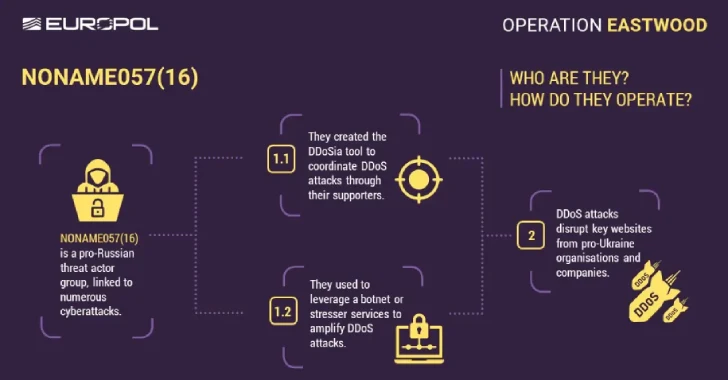
Europol Disrupts NoName057(16) Hacktivist Group Linked to DDoS Attacks Against Ukraine Europol Disrupts NoName057(16) Hacktivist Group Linked to DDoS Attacks Against Ukraine The Hacker News
Npm Packages Exploit Crypto Keys and CI Secrets Npm Packages Exploit Crypto Keys and CI Secrets The Hacker News
Cisco ASA Zero-Day Duo Under Attack; CISA Triggers Emergency Mitigation Directive Cisco ASA Zero-Day Duo Under Attack; CISA Triggers Emergency Mitigation Directive The Hacker News
Chaos RAT Malware Targets Windows and Linux via Fake Network Tool Downloads Chaos RAT Malware Targets Windows and Linux via Fake Network Tool Downloads The Hacker News
Iranian Hacker Pleads Guilty in  Million Robbinhood Ransomware Attack on Baltimore Iranian Hacker Pleads Guilty in $19 Million Robbinhood Ransomware Attack on Baltimore The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • ARTEX AI Revolutionizes Cyber Attacks on Enterprises
  • Data Breach at Frontline Education Affects Over 1.3 Million
  • Gorbag Hackers Exploit WinRAR Vulnerability to Steal Data
  • Hackers Exploit Fake ChatGPT Apps to Spread Malware
  • Node-RED Vulnerability Exploited by Hackers: Key Insights

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • ARTEX AI Revolutionizes Cyber Attacks on Enterprises
  • Data Breach at Frontline Education Affects Over 1.3 Million
  • Gorbag Hackers Exploit WinRAR Vulnerability to Steal Data
  • Hackers Exploit Fake ChatGPT Apps to Spread Malware
  • Node-RED Vulnerability Exploited by Hackers: Key Insights

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark