Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Mitigating Onboarding Risks: Secure Password Practices

Mitigating Onboarding Risks: Secure Password Practices

Posted on June 15, 2026 By CWS

Amid the hustle of onboarding new employees, IT teams often face the challenge of ensuring secure access to systems. Managing devices, accounts, and permissions within tight deadlines can lead to shortcuts in password security, presenting cyber risks.

Understanding the Risks of Temporary Onboarding Passwords

New employees frequently receive temporary passwords via email or SMS to access systems initially. However, these credentials often persist beyond their intended lifespan, posing a security threat. The convenience of sending passwords in plain text can be exploited by cyber attackers if intercepted.

Verbal password sharing attempts to mitigate digital interception risks but introduces logistical hurdles. Coordinating schedules for in-person or phone communication can complicate onboarding, and involving multiple parties increases the risk of mishandling credentials.

Securing Onboarding with Advanced Solutions

Specialized solutions like Specops First Day Password offer a secure alternative by eliminating the need for temporary passwords. Employees create their own passwords through a secure enrollment process, using a verification link sent to their personal email or mobile device.

This method enhances security by ensuring that passwords align with organizational policies from the start, reducing the risk of unauthorized access through mishandled credentials.

The Consequences of Weak Onboarding Practices

Failure to update temporary credentials can lead to significant security breaches. Notable incidents highlight the vulnerabilities of default or weak passwords, such as the 2023 attack on a Pennsylvania water authority using default PLC credentials, and a breach of McDonald’s hiring platform due to weak admin account security.

These examples underscore the critical need for robust password management strategies during the onboarding process, as temporary credentials can become long-term weaknesses if not promptly updated.

To safeguard systems, organizations should integrate secure password management solutions like Specops, which facilitate password creation and policy enforcement throughout the user lifecycle. By empowering users to generate secure passwords from day one, IT teams can enhance security while streamlining the onboarding process.

For more information on strengthening your organization’s password security, consider exploring solutions like Specops. Interested in learning more? Schedule a demo today and see how these tools can transform your onboarding processes.

Stay informed with our latest content by following us on Google News, Twitter, and LinkedIn.
The Hacker News Tags:credential management, cyber threats, Cybersecurity, digital security, employee onboarding, enrollment process, IT teams, Onboarding, password management, password security, Specops, Specops uReset, technology solutions, temporary passwords, user lifecycle

Post navigation

Previous Post: Severe Wazuh Flaw Allows Critical Security Breaches
Next Post: Ukrainian Man Admits Guilt in US for Conti Ransomware

Related Posts

Firefox Patches 2 Zero-Days Exploited at Pwn2Own Berlin with 0K in Rewards Firefox Patches 2 Zero-Days Exploited at Pwn2Own Berlin with $100K in Rewards The Hacker News
Researchers Uncover Batavia Windows Spyware Stealing Documents from Russian Firms Researchers Uncover Batavia Windows Spyware Stealing Documents from Russian Firms The Hacker News
Qualcomm Fixes 3 Zero-Days Used in Targeted Android Attacks via Adreno GPU Qualcomm Fixes 3 Zero-Days Used in Targeted Android Attacks via Adreno GPU The Hacker News
Choosing the Right Exposure Management Platform Choosing the Right Exposure Management Platform The Hacker News
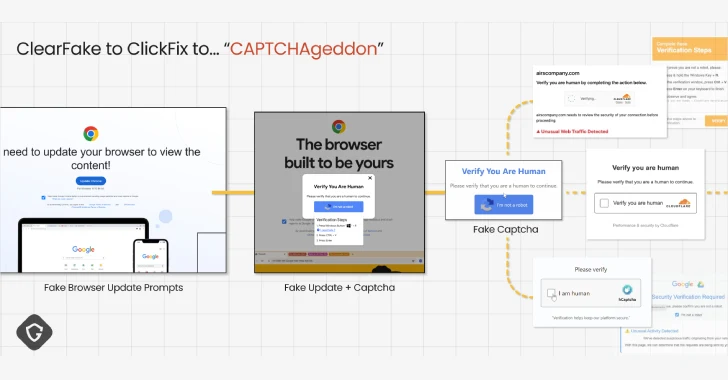
ClickFix Malware Campaign Exploits CAPTCHAs to Spread Cross-Platform Infections ClickFix Malware Campaign Exploits CAPTCHAs to Spread Cross-Platform Infections The Hacker News
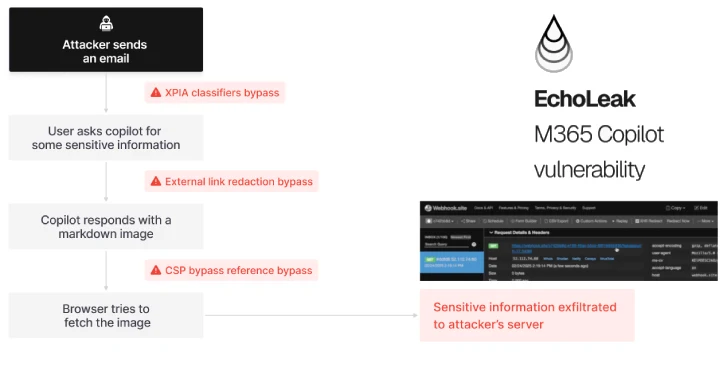
Zero-Click AI Vulnerability Exposes Microsoft 365 Copilot Data Without User Interaction Zero-Click AI Vulnerability Exposes Microsoft 365 Copilot Data Without User Interaction The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical Cisco SD-WAN Flaw Exploited by Hackers to Deploy Malware
  • Quantum Trust Hub Enhances Cryptographic Management
  • Critical GitLab Vulnerability Attempted on Alpine Linux
  • Cloudflare’s Report Unveils 8,200 Hourly DDoS Attacks
  • Massive DHS Employee Data Breach Unveiled Online

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical Cisco SD-WAN Flaw Exploited by Hackers to Deploy Malware
  • Quantum Trust Hub Enhances Cryptographic Management
  • Critical GitLab Vulnerability Attempted on Alpine Linux
  • Cloudflare’s Report Unveils 8,200 Hourly DDoS Attacks
  • Massive DHS Employee Data Breach Unveiled Online

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark