Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Phishing Attack Uses Stolen Credentials to Install LogMeIn RMM for Persistent Access

Phishing Attack Uses Stolen Credentials to Install LogMeIn RMM for Persistent Access

Posted on January 23, 2026January 23, 2026 By CWS

Ravie LakshmananJan 23, 2026Email Safety / Endpoint Safety
Cybersecurity researchers have disclosed particulars of a brand new dual-vector marketing campaign that leverages stolen credentials to deploy reliable Distant Monitoring and Administration (RMM) software program for persistent distant entry to compromised hosts.
“As a substitute of deploying customized viruses, attackers are bypassing safety perimeters by weaponizing the mandatory IT instruments that directors belief,” KnowBe4 Menace Labs researchers Jeewan Singh Jalal, Prabhakaran Ravichandhiran, and Anand Bodke stated. “By stealing a ‘skeleton key’ to the system, they flip reliable Distant Monitoring and Administration (RMM) software program right into a persistent backdoor.”
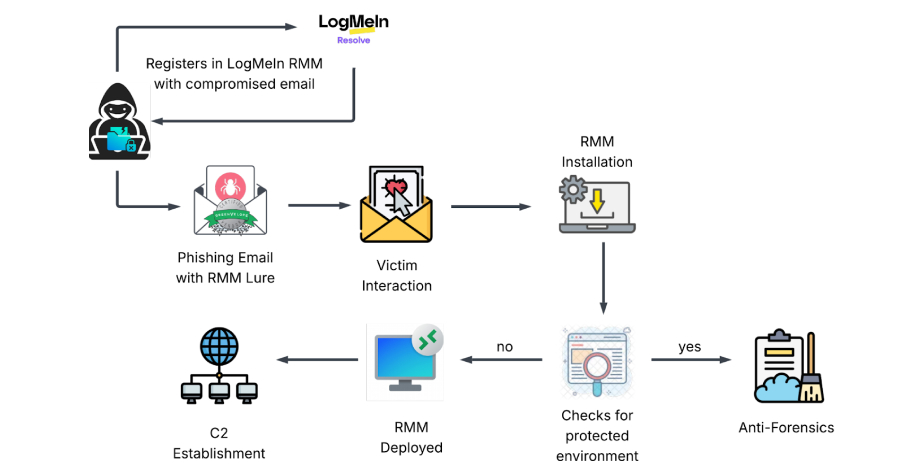
The assault unfolds in two distinct waves, the place the risk actors leverage faux invitation notifications to steal sufferer credentials, after which leverage these pilfered credentials to deploy RMM instruments to determine persistent entry.

The bogus emails are disguised as an invite from a reliable platform known as Greenvelope, and goal to trick recipients into clicking on a phishing URL that is designed to reap their Microsoft Outlook, Yahoo!, AOL.com login data. As soon as this data is obtained, the assault strikes to the subsequent part.
Particularly, this entails the risk actor registering with LogMeIn utilizing the compromised e mail to generate RMM entry tokens, that are then deployed in a follow-on assault by an executable named “GreenVelopeCard.exe” to determine persistent distant entry to sufferer techniques.
The binary, signed with a legitimate certificates, comprises a JSON configuration that acts as a conduit to silently set up LogMeIn Resolve (previously GoTo Resolve) and connect with an attacker-controlled URL with out the sufferer’s data.
With the RMM instrument now deployed, the risk actors weaponize the distant entry to change its service settings in order that it runs with unrestricted entry on Home windows. The assault additionally establishes hidden scheduled duties to robotically launch the RMM program even when it is manually terminated by the consumer.
To counter the risk, it is suggested that organizations monitor for unauthorized RMM installations and utilization patterns.

The Hacker News Tags:Access, Attack, Credentials, Install, LogMeIn, Persistent, Phishing, RMM, Stolen

Post navigation

Previous Post: TrustAsia Revoked 143 Certificates Following LiteSSL ACME Service Vulnerability
Next Post: New Windows Notepad and Paint Update Brings More Useful AI Features

Related Posts

Langflow Vulnerabilities Allow Remote Code Execution Langflow Vulnerabilities Allow Remote Code Execution The Hacker News
AI-Enhanced Attack Exploits PHP2Shell in European Government Breach AI-Enhanced Attack Exploits PHP2Shell in European Government Breach The Hacker News
What Security Leaders Need to Know in 2025 What Security Leaders Need to Know in 2025 The Hacker News
UNC6384 Deploys PlugX via Captive Portal Hijacks and Valid Certificates Targeting Diplomats UNC6384 Deploys PlugX via Captive Portal Hijacks and Valid Certificates Targeting Diplomats The Hacker News
Azure Cosmos DB Vulnerability Could Access Databases Azure Cosmos DB Vulnerability Could Access Databases The Hacker News
Critical Adobe Campaign Flaws Patched to Prevent Code Execution Critical Adobe Campaign Flaws Patched to Prevent Code Execution The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity
  • SGLang Exploit Breach Exposes NEAR AI User Data
  • Ivanti Releases Critical Security Updates for Key Products
  • Microsoft’s November Patch Tuesday Fixes 1,094 Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity
  • SGLang Exploit Breach Exposes NEAR AI User Data
  • Ivanti Releases Critical Security Updates for Key Products
  • Microsoft’s November Patch Tuesday Fixes 1,094 Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark