Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Azure Cosmos DB Vulnerability Could Access Databases

Azure Cosmos DB Vulnerability Could Access Databases

Posted on July 30, 2026 By CWS

A recently patched vulnerability in Azure Cosmos DB posed a significant security risk, potentially allowing unauthorized access to customer databases. Discovered by cloud security firm Wiz, the flaw could have enabled attackers to bypass the service’s Gremlin query sandbox, thereby gaining full read and write access to databases across different customer tenants.

Details of the CosmosEscape Exploit

Wiz, which identified and named the exploit chain as ‘CosmosEscape’, revealed that the attack could commence with a specially crafted query targeting a Gremlin database under the attacker’s control. This breach allowed code execution on a multi-tenant gateway, revealing a platform-wide signing secret and a regional account directory. These vulnerabilities facilitated the identification of target databases and the extraction of their primary account keys.

Microsoft responded promptly by blocking the vulnerable Gremlin entry point within 48 hours following Wiz’s report in November 2025. A comprehensive fix was implemented by July 2026, effectively removing the platform-wide key. Notably, Microsoft confirmed that there was no unauthorized data access beyond the researchers’ controlled testing, assuring users that no further action was required.

Technical Insights into the Vulnerability

The technical analysis by Wiz highlights that the Cosmos DB’s custom Gremlin engine translates queries into .NET code, executing them in a restricted environment. However, the imposed restrictions did not adequately prevent .NET reflection, which allowed researchers to execute arbitrary code by constructing file-read and file-write operations. The execution occurred on a component termed the DB Gateway, responsible for processing queries on multi-tenant Azure Service Fabric clusters.

Significantly, the DB Gateway was equipped with credentials that provided access to what Wiz dubbed the ‘Cosmos Master Key’. This key could extract the primary key for any account, spanning multiple tenants, regions, and APIs, including SQL, MongoDB, Cassandra, and Gremlin. Furthermore, access to a regional database named the Config Store was possible, which contained essential account details and network settings.

Future Implications and Security Measures

Despite the potential for widespread access, Wiz confirmed that no private or network-isolated accounts were compromised. The researchers did suggest that network settings could be altered, though such actions were not demonstrated against other customer accounts. Microsoft’s documentation notes that Cosmos DB holds critical data for products like Microsoft Teams and Copilot, although no unauthorized access to such data was reported.

The specific timeline for the vulnerability’s presence in production remains unclear, as does the complete scope of Microsoft’s log review. However, the security flaw, identified separately from past issues like ChaosDB and CosMiss, was effectively closed, mitigating further risk. This incident underscores the critical importance of robust security practices in cloud services and the swift action required to address vulnerabilities.
The Hacker News Tags:Azure, cloud computing, cloud security, Cosmos DB, Cybersecurity, data access, Database Flaw, database security, Gremlin Query, Microsoft, network security, security patch, tech news, Vulnerability, Wiz

Post navigation

Previous Post: Global Outage Affects Claude AI Users with Overload Errors
Next Post: Discern Security Secures $13M in Series A Funding

Related Posts

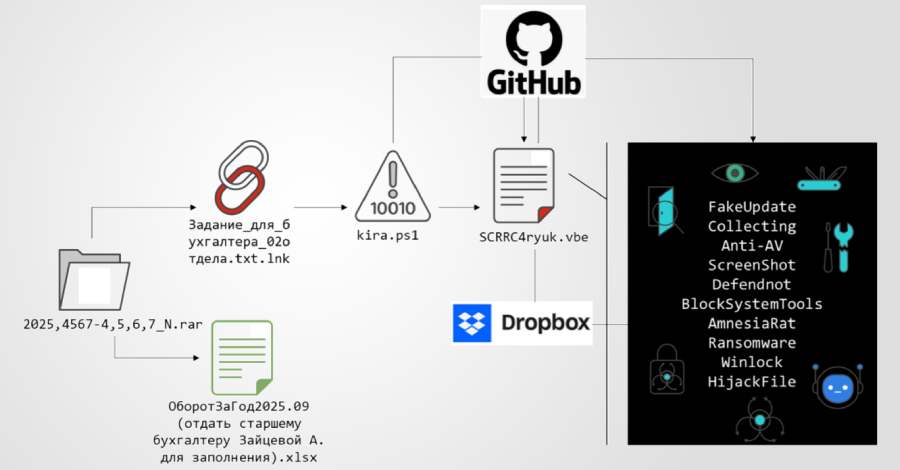
Multi-Stage Phishing Campaign Targets Russia with Amnesia RAT and Ransomware Multi-Stage Phishing Campaign Targets Russia with Amnesia RAT and Ransomware The Hacker News
Critical Security Threats and Global Cyber Developments Critical Security Threats and Global Cyber Developments The Hacker News
5 Critical Questions For Adopting an AI Security Solution 5 Critical Questions For Adopting an AI Security Solution The Hacker News
Hack-for-Hire Campaign Targets MENA Journalists Hack-for-Hire Campaign Targets MENA Journalists The Hacker News
Chinese Hackers Exploit Trimble Cityworks Flaw to Infiltrate U.S. Government Networks Chinese Hackers Exploit Trimble Cityworks Flaw to Infiltrate U.S. Government Networks The Hacker News
North Korean Hackers Deploy 197 npm Packages to Spread Updated OtterCookie Malware North Korean Hackers Deploy 197 npm Packages to Spread Updated OtterCookie Malware The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Critical Vulnerabilities in Dell ObjectScale Systems Discovered
  • AI Industry Urged to Prioritize Safety to Prevent Potential Risks
  • Passkey Phishing Exploits Target Microsoft Cloud Accounts
  • Plesk Backup Manager Vulnerability Exposes Servers to Risk
  • Revolut Data Breach: Sensitive Customer Info Exposed

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Critical Vulnerabilities in Dell ObjectScale Systems Discovered
  • AI Industry Urged to Prioritize Safety to Prevent Potential Risks
  • Passkey Phishing Exploits Target Microsoft Cloud Accounts
  • Plesk Backup Manager Vulnerability Exposes Servers to Risk
  • Revolut Data Breach: Sensitive Customer Info Exposed

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark