Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
TP-Link Patches Four Omada Gateway Flaws, Two Allow Remote Code Execution

TP-Link Patches Four Omada Gateway Flaws, Two Allow Remote Code Execution

Posted on October 22, 2025October 22, 2025 By CWS

Oct 22, 2025Ravie LakshmananVulnerability / Community Safety
TP-Hyperlink has launched safety updates to handle 4 safety flaws impacting Omada gateway units, together with two crucial bugs that would end in arbitrary code execution.
The vulnerabilities in query are listed under –

CVE-2025-6541 (CVSS rating: 8.6) – An working system command injection vulnerability that might be exploited by an attacker who can log in to the online administration interface to run arbitrary instructions
CVE-2025-6542 (CVSS rating: 9.3) – An working system command injection vulnerability that might be exploited by a distant unauthenticated attacker to run arbitrary instructions
CVE-2025-7850 (CVSS rating: 9.3) – An working system command injection vulnerability that might be exploited by an attacker in possession of an administrator password of the online portal to run arbitrary instructions
CVE-2025-7851 (CVSS rating: 8.7) – An improper privilege administration vulnerability that might be exploited by an attacker to acquire the basis shell on the underlying working system below restricted circumstances

“Attackers could execute arbitrary instructions on the system’s underlying working system,” TP-Hyperlink mentioned in an advisory launched Tuesday.
The problems affect the next product fashions and variations –

ER8411
ER7412-M2
ER707-M2
ER7206
ER605
ER706W
ER706W-4G
ER7212PC
G36
G611
FR365
FR205
FR307-M2

Whereas TP-Hyperlink makes no point out of the failings being exploited within the wild, it is suggested that customers transfer rapidly to obtain and replace to the most recent firmware to repair the vulnerabilities.
“Test the configurations of the system after the firmware improve to make sure that all settings stay correct, safe, and aligned with their meant preferences,” it added.
It additionally famous in a disclaimer that it can’t bear any duty for any penalties that will come up if the aforementioned advisable actions should not adhered to.

The Hacker News Tags:Code, Execution, Flaws, Gateway, Omada, Patches, Remote, TPLink

Post navigation

Previous Post: Chrome V8 JavaScript Engine Vulnerability Let Attackers Execute Remote Code
Next Post: Threat Actors Compromise Xubuntu Website To Deliver Malicious Windows Executable

Related Posts

SmartLoader Malware Exploits Oura Server for Data Theft SmartLoader Malware Exploits Oura Server for Data Theft The Hacker News
German Agencies Issue Alert on Signal Phishing Threat German Agencies Issue Alert on Signal Phishing Threat The Hacker News
Firewall Flaws, AI-Built Malware, Browser Traps, Critical CVEs & More Firewall Flaws, AI-Built Malware, Browser Traps, Critical CVEs & More The Hacker News
Ex-Google Engineer Convicted for Stealing 2,000 AI Trade Secrets for China Startup Ex-Google Engineer Convicted for Stealing 2,000 AI Trade Secrets for China Startup The Hacker News
Hackers Exploit Misconfigured Docker APIs to Mine Cryptocurrency via Tor Network Hackers Exploit Misconfigured Docker APIs to Mine Cryptocurrency via Tor Network The Hacker News
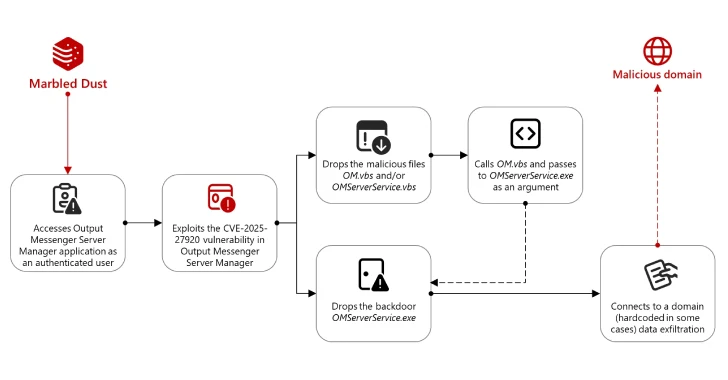
Türkiye Hackers Exploited Output Messenger Zero-Day to Drop Golang Backdoors on Kurdish Servers Türkiye Hackers Exploited Output Messenger Zero-Day to Drop Golang Backdoors on Kurdish Servers The Hacker News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark