Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Spirals Ransomware Quickly Hits IT Firm with Web Shell

Spirals Ransomware Quickly Hits IT Firm with Web Shell

Posted on July 18, 2026 By CWS

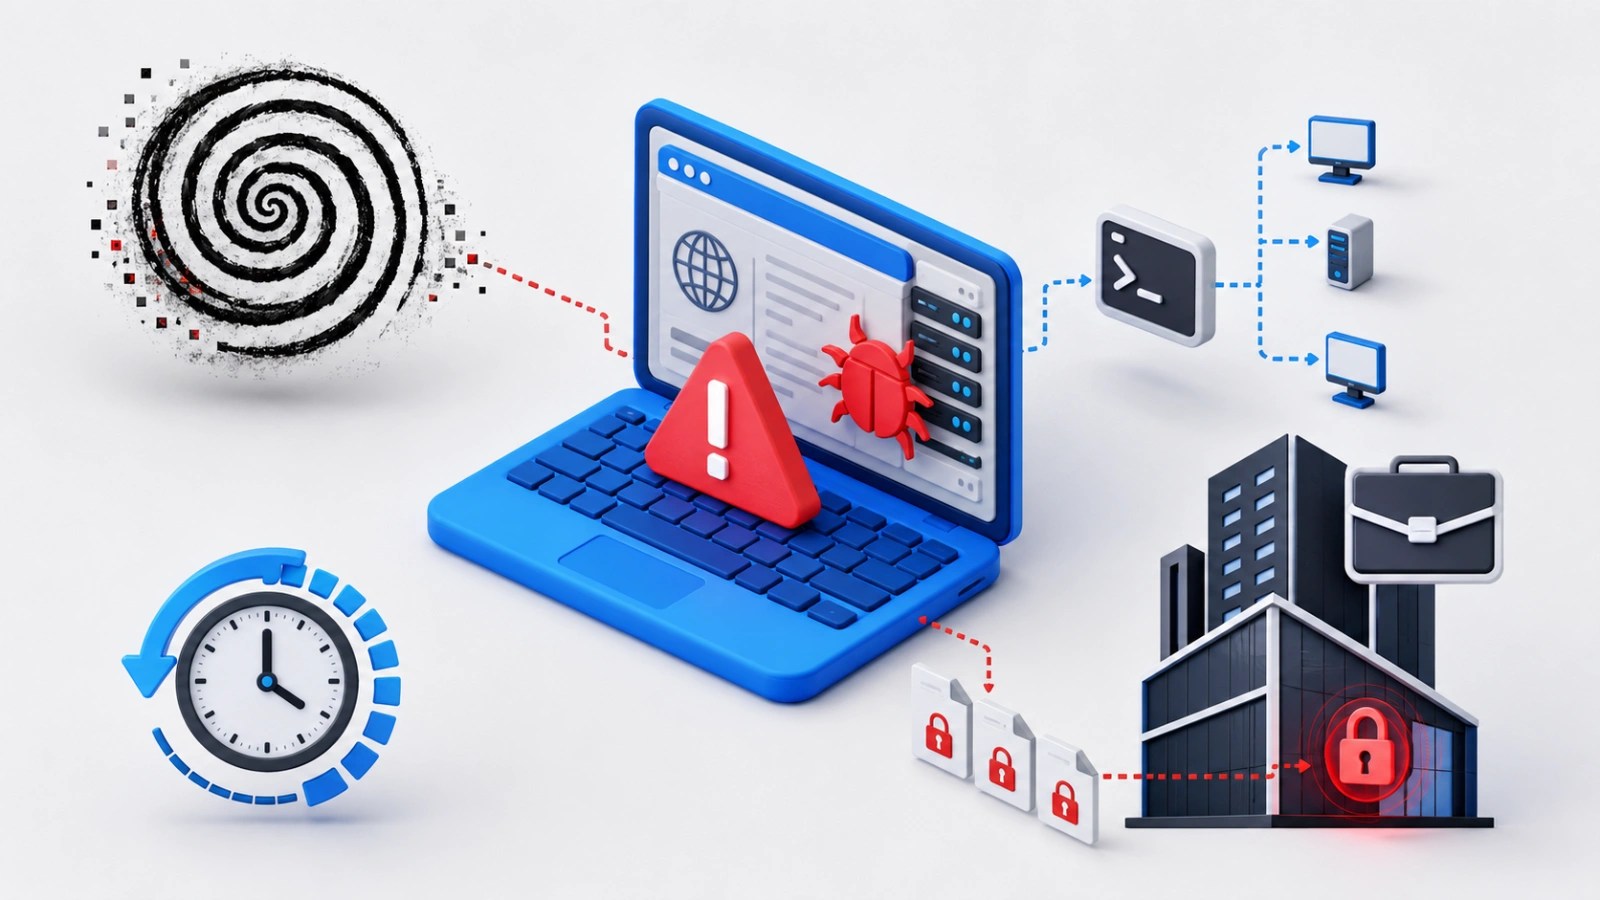
A newly identified ransomware known as ‘Spirals’ targeted an IT services firm in South Asia in June 2026. According to Symantec’s Threat Hunter Team, the attackers infiltrated the company’s systems and encrypted the network within less than a day.

Developed using Rust, the Spirals payload appears to be either a new creation or specifically designed for this assault, with the assailants yet to be identified.

Web Shell and PsExec Utilization

The attack commenced on June 16 at 22:21 local time. The perpetrators breached an internet-facing IIS web server, deploying an ASP.NET web shell. Within a short timeframe, three tunneling tools were activated, including Chisel masquerading as chrome.exe, alongside a Cloudflare tunnel client, to establish secret communication channels. A token impersonation tool was also used, likely aiding in privilege escalation.

During an intense three-hour session, the attacker manipulated cmd.exe and powershell.exe through the IIS worker process, bypassed User Account Control (UAC), enabled Remote Desktop Protocol (RDP), created a persistent local account, and extracted the SAM hive. By 23:07, efforts to neutralize security systems were evident.

Lateral Movement and Mass Deployment

By 23:33, the attackers transitioned to using WMI-based lateral movement, quickly compromising over a dozen systems using stolen domain administrator credentials, indicating a pre-planned, automated approach rather than manual exploration.

The following day, on June 17, the attackers shifted to PsExec for mass payload deployment. Starting around 14:12, a compromised system distributed a base64-encoded PowerShell payload to network targets every few seconds for 30 minutes. This payload disabled Windows Defender’s real-time monitoring and halted over 20 critical services.

Encryption Tactics and Defensive Measures

The ransomware executed under the guise of bitsadmin.exe, a legitimate Windows utility, was strategically distributed across network locations to ensure widespread propagation. This tactic highlights the need for organizations to audit internal script shares.

Spirals, a Rust-based encryptor, comes equipped with defense evasion, lateral movement, and privilege escalation capabilities. It employs AES-128 for file encryption and an attacker-controlled ECDH P-256 public key to secure local AES keys.

The ransom note, C:RECOVERY_SECTION.log, threatens data exposure within six days if payment is not made, directing victims to a Tor-based negotiation portal.

Though Spirals has only been observed in one instance, its sophisticated operations suggest the potential for broader attacks. Organizations should prioritize web shell detection, behavioral auditing of WMI and PsExec activities, and the protection of credentials against LSASS memory dumping tools.

Cyber Security News Tags:cyber attack, cyber threat, IIS web shell, IT security, IT services, network encryption, PsExec, Rust-based ransomware, Spirals ransomware, Symantec

Post navigation

Previous Post: Critical Vulnerabilities in Citrix Clients Pose Security Risks
Next Post: Hugging Face Thwarts AI-Powered Cyber Attack

Related Posts

Top Cybersecurity Firms to Watch at 2026 Gartner Summit Top Cybersecurity Firms to Watch at 2026 Gartner Summit Cyber Security News
Cyberattack on Novo Nordisk Exposes Medical and AI Data Cyberattack on Novo Nordisk Exposes Medical and AI Data Cyber Security News
U.S. Ends Export Controls on Claude Fable 5 AI Model U.S. Ends Export Controls on Claude Fable 5 AI Model Cyber Security News
Threat Actors Leverage Several RMM Tools in Phishing Attack to Maintain Remote Access Threat Actors Leverage Several RMM Tools in Phishing Attack to Maintain Remote Access Cyber Security News
Top 10 Best Dynamic Application Security Testing (DAST) Platforms in 2025 Top 10 Best Dynamic Application Security Testing (DAST) Platforms in 2025 Cyber Security News
AI Security Testing Evolves with New Threats AI Security Testing Evolves with New Threats Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Claude AI Unravels 25-Year NSA Cryptography Enigma Swiftly
  • Hackers Breach Microsoft 365 Using ConnectWise Backup
  • Israeli Firm’s Role in Global Spyware Campaign Uncovered
  • Malicious npm Package ‘imgdecode’ Found in Supply Chain Attack
  • Critical Flaw in Collabora Online Jeopardizes Nextcloud Security

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Claude AI Unravels 25-Year NSA Cryptography Enigma Swiftly
  • Hackers Breach Microsoft 365 Using ConnectWise Backup
  • Israeli Firm’s Role in Global Spyware Campaign Uncovered
  • Malicious npm Package ‘imgdecode’ Found in Supply Chain Attack
  • Critical Flaw in Collabora Online Jeopardizes Nextcloud Security

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark