Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
AI Discovers Critical Linux Kernel Vulnerability

AI Discovers Critical Linux Kernel Vulnerability

Posted on September 30, 2026 By CWS

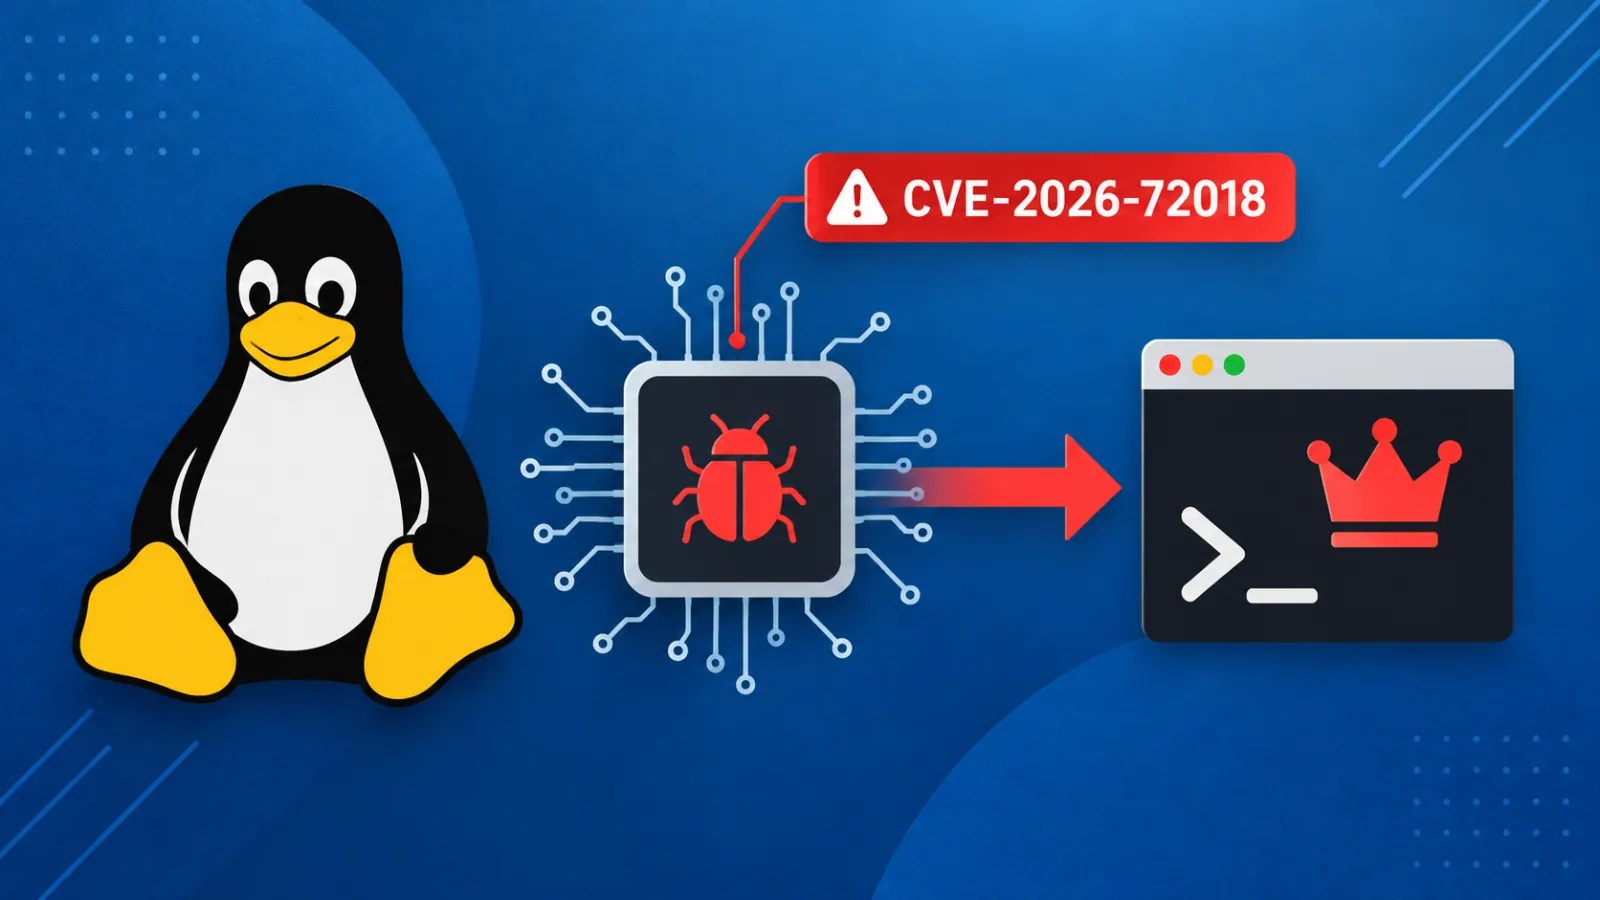
The autonomous security research platform XBOW has revealed a critical vulnerability, identified as CVE-2026-72018, in the Linux kernel. This flaw, found in the DIBS loopback implementation used by the SMC-D shared-memory communication path, poses significant security risks by allowing a limited out-of-bounds memory write to escalate local privileges to root access.

Understanding the Security Flaw

This vulnerability arises from a missing bounds check, which permits attacker-controlled data to exceed the allocated buffer in the kernel. Despite the exploit’s limited capacity to produce only 16 zero bytes at a specific memory offset, the researchers developed a method to elevate privileges without needing an additional information leak.

The affected component, the dibs_loopback driver, facilitates Shared Memory Communications Direct (SMC-D) on standard x86 Linux systems. Originally linked with IBM mainframe environments, the SMC-D’s exposure on commodity Linux systems through loopback networking has turned previously difficult-to-access code into a vulnerable attack surface.

Exploit Mechanics and Mitigation

XBOW’s findings detailed how a manipulated dmbe_idx value could alter offset calculations during the SMC connection setup. This issue culminates in the move_data() routine, where a memcpy() operation occurs without proper validation of the offset and size. The recent updates have introduced validation checks to prevent such out-of-bounds writes.

The exploit leverages the Linux kernel’s cred structure, where zeroing out certain fields, such as the effective user ID (euid), results in root privileges. Although the write is not arbitrary, its ability to reset security-sensitive states can lead to successful privilege escalation.

Implications and Recommendations

XBOW’s proof of concept demonstrated a success rate of 22 out of 100 attempts, emphasizing both the potential and the limits of automated vulnerability research. The vulnerability carries a CVSS score of 7.8, indicating high severity due to its impact on confidentiality, integrity, and availability.

Organizations are advised to implement the Linux kernel updates that address this vulnerability. Additional precautions include reviewing workloads and containers that have been granted the CAP_NET_ADMIN capability, as it plays a crucial role in the attack vector.

Overall, while AI-driven research showcases the ability to perform extensive code analysis, human intervention remains crucial in refining exploit strategies and ensuring effective threat mitigation. Administrators should stay vigilant and apply necessary updates promptly to safeguard their systems.

Cyber Security News Tags:AI, CVE, CVE-2026-72018, Cybersecurity, DIBS loopback, Exploit, kernel bug, kernel vulnerability, Linux, privilege escalation, root access, Security, security research, SMC-D, vulnerability discovery

Post navigation

Previous Post: Chrome and Firefox Updates Fix Over 100 Security Flaws

Related Posts

Microsoft Ends Unwanted Ads in Windows 11 Microsoft Ends Unwanted Ads in Windows 11 Cyber Security News
Why Real-Time Threat Intelligence Is Critical for Modern SOCs Why Real-Time Threat Intelligence Is Critical for Modern SOCs Cyber Security News
Gonjeshke Darande Threat Actors Pose as Hacktivist Infiltrated Iranian Crypto Exchange Gonjeshke Darande Threat Actors Pose as Hacktivist Infiltrated Iranian Crypto Exchange Cyber Security News
Chinese Hackers Exploit Routers for Hidden Cyber Attacks Chinese Hackers Exploit Routers for Hidden Cyber Attacks Cyber Security News
ShowDoc Vulnerability Exploited by Cybercriminals ShowDoc Vulnerability Exploited by Cybercriminals Cyber Security News
Vulnerabilities in Preinstalled Android Apps Expose PIN Codes and Allow Command Injection Vulnerabilities in Preinstalled Android Apps Expose PIN Codes and Allow Command Injection Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • AI Discovers Critical Linux Kernel Vulnerability
  • Chrome and Firefox Updates Fix Over 100 Security Flaws
  • AI Coding Tools Expose Sensitive Data on GitHub
  • RATHat Malware Uses AI for Advanced Android Control
  • AI Liability Concerns Rise Amid OpenAI Legal Challenges

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • AI Discovers Critical Linux Kernel Vulnerability
  • Chrome and Firefox Updates Fix Over 100 Security Flaws
  • AI Coding Tools Expose Sensitive Data on GitHub
  • RATHat Malware Uses AI for Advanced Android Control
  • AI Liability Concerns Rise Amid OpenAI Legal Challenges

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark