Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
RATHat Malware Uses AI for Advanced Android Control

RATHat Malware Uses AI for Advanced Android Control

Posted on September 30, 2026 By CWS

Introduction to RATHat Malware

The RATHat malware has emerged as a significant threat to Android devices, leveraging Gemini AI to extend its control beyond typical app permissions. This sophisticated banking trojan exploits a developer feature to establish a persistent command channel, remaining active even after the malicious app is removed, until the device is restarted.

Distributed through malicious advertisements and phishing messages, primarily targeting regions such as Europe, Latin America, and Southeast Asia, RATHat cleverly deceives users into granting Accessibility access. This grants the malware extensive control over the device, surpassing earlier iterations of similar threats.

Distribution and Evolution of RATHat

Cybersecurity researchers from Cleafy have identified three iterations of the RATHat operator panel between April and September 2026. Despite retaining a consistent design, the underlying infrastructure has evolved significantly. Earlier campaigns disguised the malware as cryptocurrency trading and adult content apps.

According to Cleafy, nearly 100 distinct deployments have been detected since April 2026, highlighting the malware’s widespread reach. The use of licensing restrictions and parallel campaigns suggests a malware-as-a-service model, indicating decentralized control over its deployments.

Technical Aspects and Capabilities

Once RATHat gains Accessibility access, it navigates through the device settings, enabling wireless debugging and reading the pairing code displayed on the screen. This allows the malware to pair with the local Android Debug Bridge service, accessing the device as the shell user, identified by UID 2000.

The pairing process involves identifying specific controls, which can fail on unfamiliar interfaces. In such cases, the malware communicates with Gemini AI, receiving real-time instructions to navigate the device interface.

Implications and Preventative Measures

RATHat’s capabilities include deploying a separate service that operates independently from the app, allowing screen content capture and touch injection without usual prompts. However, these tools are ineffective on Android 14 and later, necessitating app-based capture with user consent.

The malware’s command panel, evolving from BlackCat to Panda Workshop versions, enables operators to manage deployments and access stolen data. It also features an AI tool for analyzing SMS messages to estimate bank balances, aiding in target prioritization.

Conclusion and Future Outlook

RATHat represents a growing threat in the realm of mobile cybersecurity, with its use of AI pointing to potential future developments in automated attacks. Cleafy’s research underscores the importance of monitoring activities executed with UID 2000 and extending security measures beyond conventional app permissions.

As RATHat continues to evolve, organizations must stay vigilant, adopting advanced security protocols to safeguard against such sophisticated threats. The persistent nature of the malware, surviving until device reboot, highlights the need for continuous monitoring and proactive defense strategies.
Cyber Security News Tags:Android malware, banking trojan, cyber threats, Cybersecurity, fraud prevention, Gemini AI, malware-as-a-service, mobile attacks, mobile security, Phishing, RatHat, technology news, wireless debugging

Post navigation

Previous Post: AI Liability Concerns Rise Amid OpenAI Legal Challenges
Next Post: AI Coding Tools Expose Sensitive Data on GitHub

Related Posts

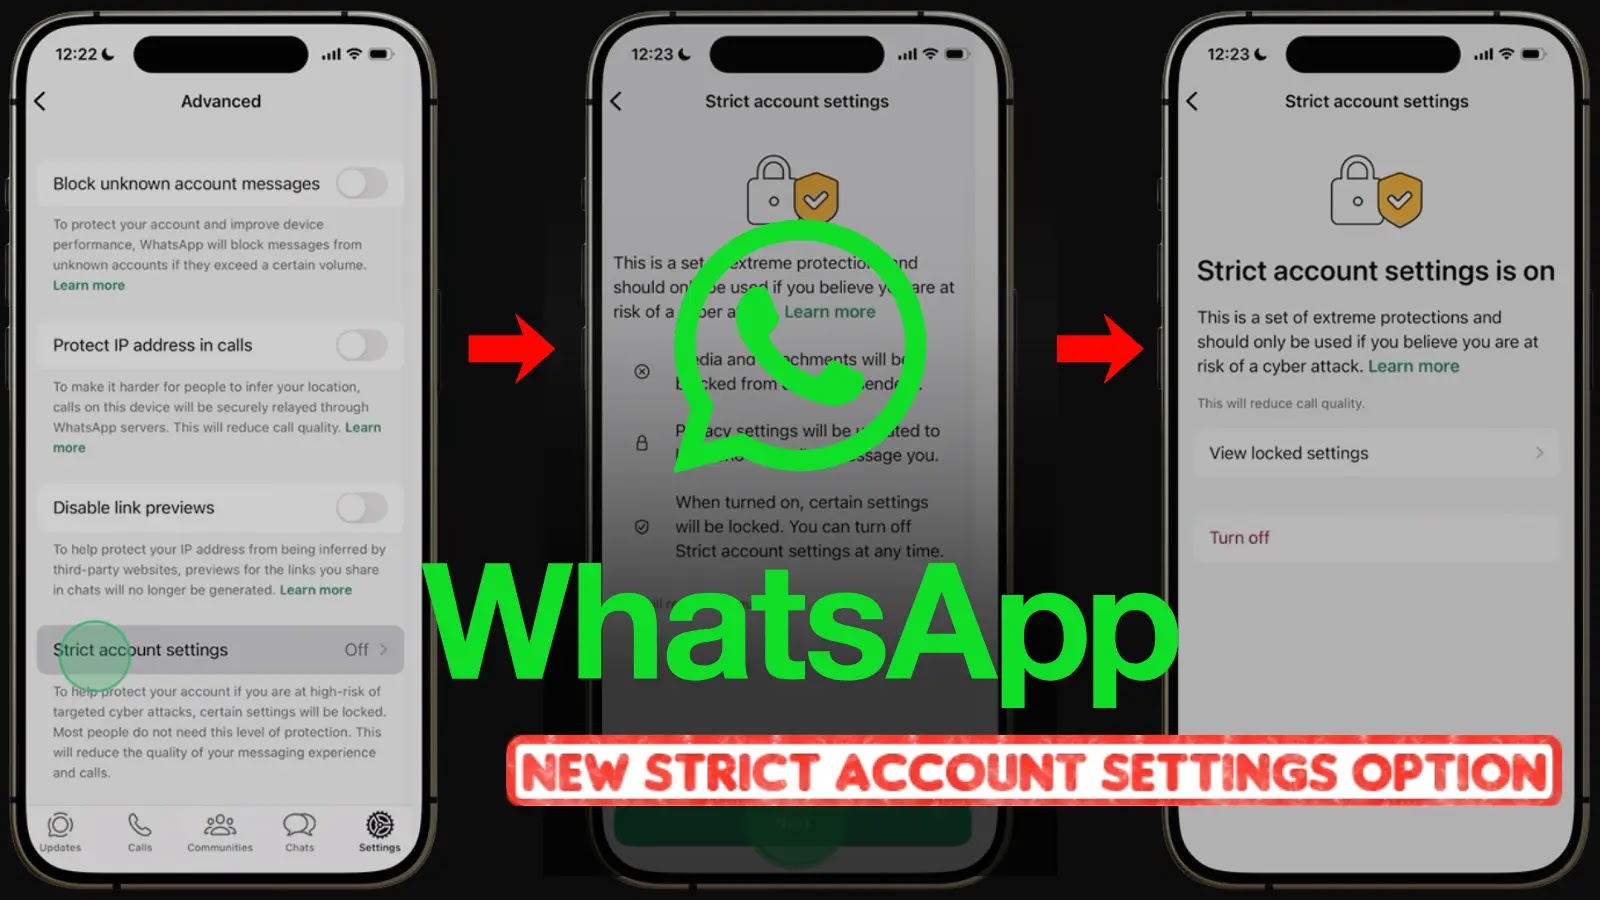
WhatsApp New Strict Account Settings Option to Protect Your Account from Hackers WhatsApp New Strict Account Settings Option to Protect Your Account from Hackers Cyber Security News
CRESCENTHARVEST Malware Targets Iran Protesters CRESCENTHARVEST Malware Targets Iran Protesters Cyber Security News
OpenAI Launches Bio Bug Bounty for GPT-5.5 AI Safety OpenAI Launches Bio Bug Bounty for GPT-5.5 AI Safety Cyber Security News
VMware Cloud Foundation 9.0 Released With Modern Workloads & AI Services VMware Cloud Foundation 9.0 Released With Modern Workloads & AI Services Cyber Security News
XLoader Malware Analyzed Using ChatGPT’s, Breaks RC4 Encryption Layers in Hours XLoader Malware Analyzed Using ChatGPT’s, Breaks RC4 Encryption Layers in Hours Cyber Security News
ZiChatBot Malware Exploits Zulip APIs for Stealth Operations ZiChatBot Malware Exploits Zulip APIs for Stealth Operations Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • MATCHBOIL Deploys Backdoor via Hidden Servers
  • AhsayCBS Flaws Actively Exploited, Urgent Action Needed
  • Hackers Break Into Google Pixel 10 at Pwn2Own Contest
  • Critical Flaw in React Server Components Puts Next.js Servers at Risk
  • Android Devices with Preinstalled Malware Threaten Users Globally

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • MATCHBOIL Deploys Backdoor via Hidden Servers
  • AhsayCBS Flaws Actively Exploited, Urgent Action Needed
  • Hackers Break Into Google Pixel 10 at Pwn2Own Contest
  • Critical Flaw in React Server Components Puts Next.js Servers at Risk
  • Android Devices with Preinstalled Malware Threaten Users Globally

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark