Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Critical Vulnerability In Chromium’s Blink Let Attackers Crash Chromium-based Browsers Within Seconds

Critical Vulnerability In Chromium’s Blink Let Attackers Crash Chromium-based Browsers Within Seconds

Posted on October 30, 2025October 31, 2025 By CWS

Safety researcher Jofpin has disclosed “Brash,” a vital flaw in Google’s Blink rendering engine that permits attackers to crash Chromium-based browsers nearly immediately.

Affecting billions of customers worldwide, this architectural weak point exploits unchecked updates to the doc.title API, overwhelming the browser’s primary thread and triggering system-wide denial of service with out subtle instruments or privileges.

The vulnerability stems from Blink’s lack of price limiting on title modifications, permitting malicious JavaScript to flood the DOM with hundreds of thousands of mutations per second.

As detailed in Jofpin’s proof-of-concept on GitHub, the assault unfolds in three phases: pre-generating high-entropy strings to keep away from CPU overhead, injecting bursts of as much as 24 million updates, and saturating the UI thread till collapse.

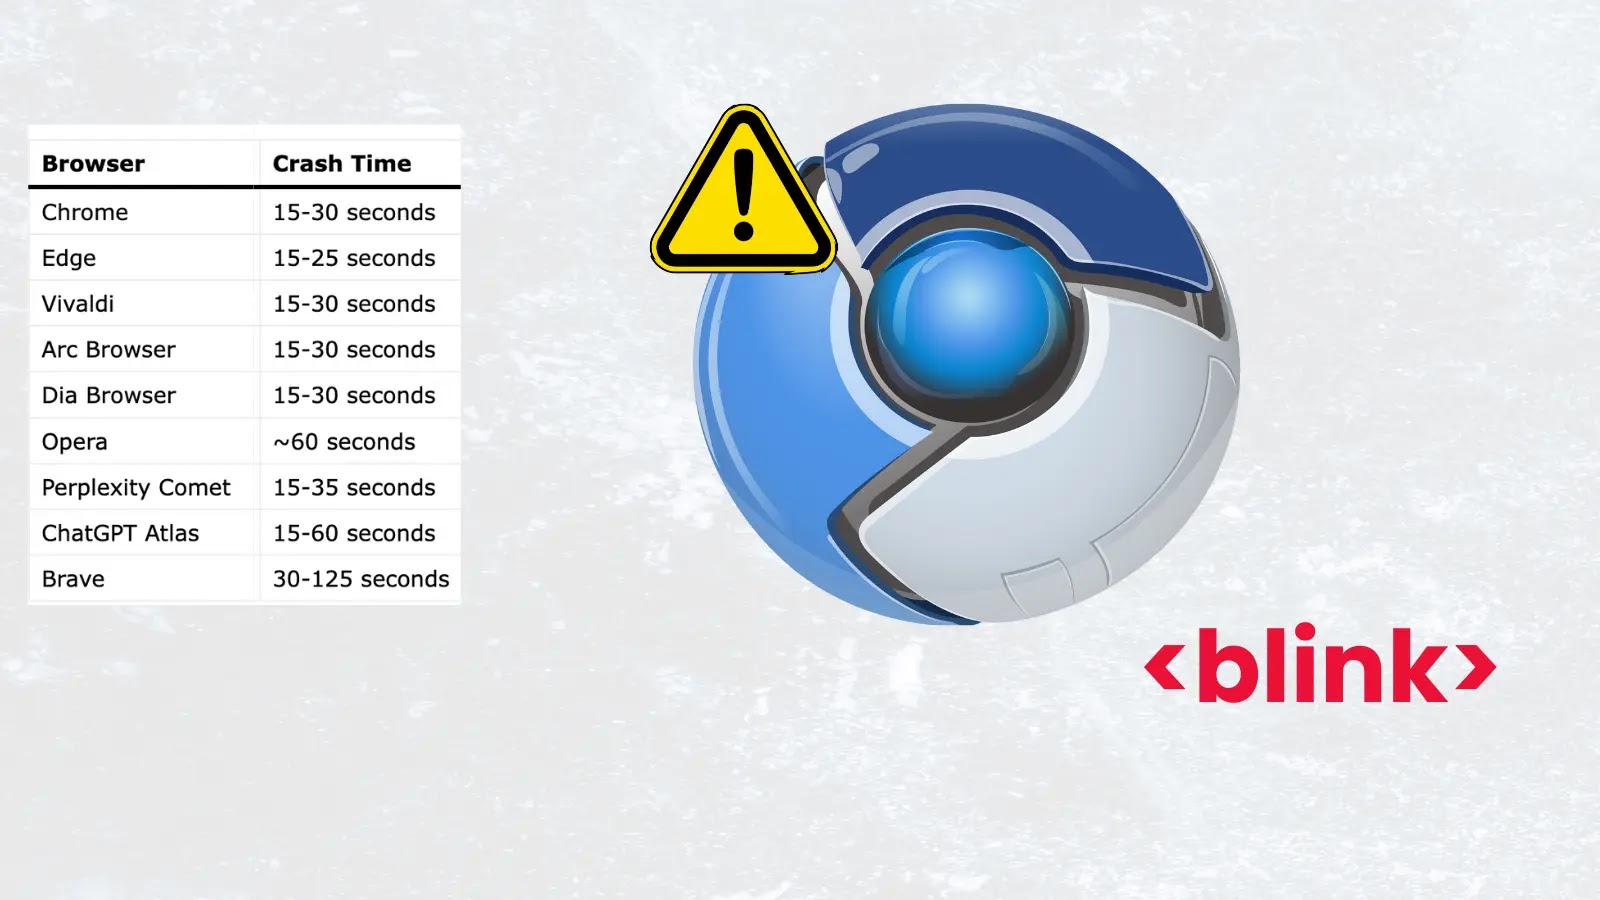
Browsers freeze inside 15 to 60 seconds, spiking CPU utilization to extremes that degrade general system efficiency and halt concurrent processes.

Examined variations as much as Chromium 143.0.7483.0 stay susceptible, together with Chrome, Edge, Opera, Courageous, and Vivaldi on desktop, Android, and embedded units.

Widespread Influence On Chromium Ecosystem

Brash’s attain is staggering, doubtlessly exposing over 3 billion web customers to disruption since Chromium powers nearly all of browsers.

On macOS, Home windows, and Linux, Chrome crashes in 15-30 seconds underneath excessive settings, whereas slower variants like Courageous take as much as two minutes.

BrowserCrash TimeChrome15-30 secondsEdge15-25 secondsVivaldi15-30 secondsArc Browser15-30 secondsDia Browser15-30 secondsOpera~60 secondsPerplexity Comet15-35 secondsChatGPT Atlas15-60 secondsBrave30-125 seconds

Non-Chromium browsers escape unscathed: Firefox’s Gecko engine and Safari’s WebKit show immune, as does iOS’s enforced WebKit coverage, which bars native Chromium apps.

The exploit’s simplicity amplifies its menace. A dwell demo at brash.run simulates the assault invisibly, whereas native PoCs let customers tweak depth reasonable for statement, excessive for fast failure.

Code snippets allow straightforward integration, with choices for delayed or scheduled triggers, turning benign pages into timed bombs.

Attackers might weaponize Brash in devastating methods. Time-delayed payloads lurk in phishing hyperlinks, activating throughout high-stakes moments like inventory trades or conferences, evading fast scans.

In AI-driven enterprises, it poisons headless browsers used for net scraping, paralyzing automated buying and selling or compliance checks.

Extra alarmingly, situations envision life-threatening chaos: a surgeon’s web-assisted process derailed mid-operation, or a flash crash on Wall Road as merchants’ terminals fail en masse throughout market open.

Banking fraud groups, too, face paralysis, permitting hundreds of thousands in unchecked transactions throughout peak volumes like Black Friday.

Jofpin emphasizes this as a design oversight, not a mere bug, urging Chromium builders to implement throttling. Because the exploit stays operational till patched, customers ought to train warning with untrusted websites.

Google has but to reply publicly, however the disclosure highlights the necessity for sturdy safeguards in core net tech.

In an period of browser-dependent operations from finance to healthcare, such flaws underscore the net’s precarious steadiness between openness and safety.

Comply with us on Google Information, LinkedIn, and X for day by day cybersecurity updates. Contact us to function your tales.
Cyber Security News Tags:Attackers, Blink, Browsers, Chromiumbased, Chromiums, Crash, Critical, Seconds, Vulnerability

Post navigation

Previous Post: Reflectiz Raises $22 Million for Website Security Solution
Next Post: Multiple Jenkins Vulnerability SAML Authentication Bypass And MCP Server Plugin Permissions

Related Posts

Beware of Weaponized Google Meet page that uses ClickFix to deliver Malicious Payload Beware of Weaponized Google Meet page that uses ClickFix to deliver Malicious Payload Cyber Security News
Arsink Rat Attacking Android Devices to Exfiltrate Sensitive Data and Enable Remote Access Arsink Rat Attacking Android Devices to Exfiltrate Sensitive Data and Enable Remote Access Cyber Security News
New Trends in Phishing Attacks Emerges as AI Reshaping the Tool used by Cybercriminals New Trends in Phishing Attacks Emerges as AI Reshaping the Tool used by Cybercriminals Cyber Security News
Hackers Exploit AI-Powered Scripts to Target Active Directory Hackers Exploit AI-Powered Scripts to Target Active Directory Cyber Security News
ownCloud Urges Users to Enable Multi-Factor Authentication Following Credential Theft ownCloud Urges Users to Enable Multi-Factor Authentication Following Credential Theft Cyber Security News
New ‘Sryxen’ Stealer Bypasses Chrome Encryption via Headless Browser Technique New ‘Sryxen’ Stealer Bypasses Chrome Encryption via Headless Browser Technique Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • 2026’s Leading Audit Management Software Platforms
  • Exploited Flaws in Openwave and Cisco BroadWorks Uncovered
  • Microsoft Releases Patches for Over 1,200 Security Flaws
  • Top Security Policy Management Tools for 2026
  • Exploited Barracuda Flaws Demand Urgent Security Updates

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • 2026’s Leading Audit Management Software Platforms
  • Exploited Flaws in Openwave and Cisco BroadWorks Uncovered
  • Microsoft Releases Patches for Over 1,200 Security Flaws
  • Top Security Policy Management Tools for 2026
  • Exploited Barracuda Flaws Demand Urgent Security Updates

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark