Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Enhancing Phishing Detection with Threat Intelligence

Enhancing Phishing Detection with Threat Intelligence

Posted on September 29, 2026 By CWS

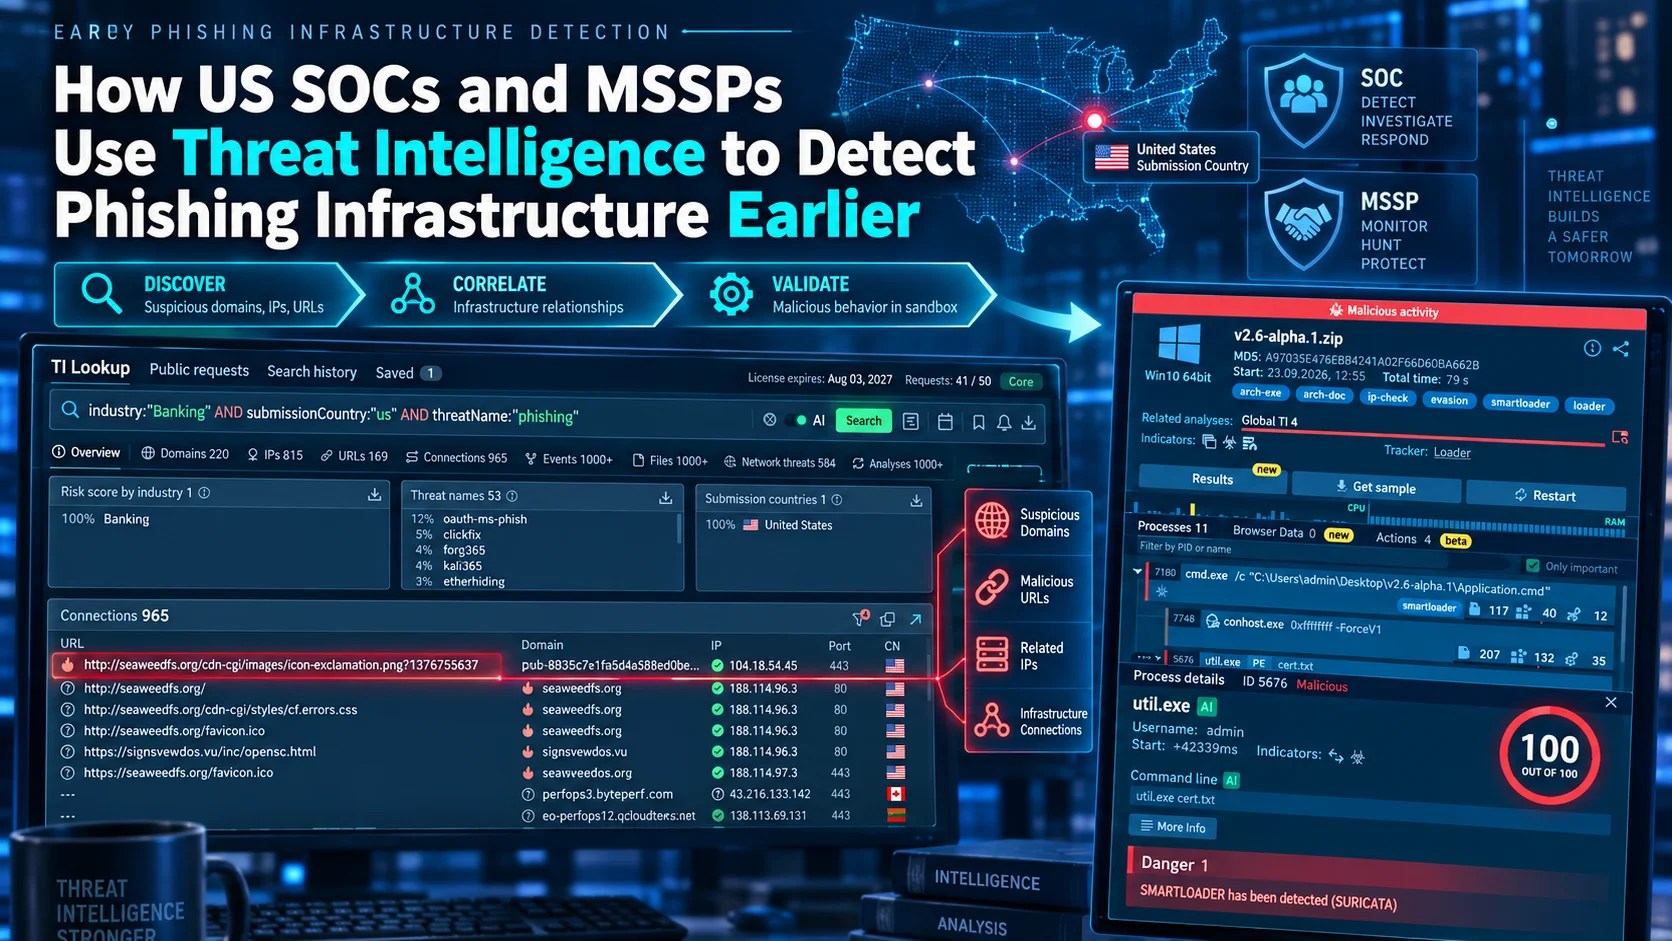
Phishing remains a significant challenge for security operations centers (SOCs) and managed security service providers (MSSPs) in the US. While the initial focus was on identifying suspicious emails, the landscape has evolved. Today, a single malicious link could lead to a newly registered domain, a compromised website, or a series of redirects, often involving legitimate cloud services that make detection more challenging.

The Complexity of Phishing Campaigns

Phishing strategies have grown more sophisticated. Attackers now utilize legitimate platforms to host content, leverage compromised websites, and employ various redirection techniques to mask their activities. Some phishing pages even adapt their behavior based on the visitor’s profile, complicating automated detection.

According to ANY.RUN’s Cyber Risk Report for the first half of 2026, OAuth device-code phishing attacks surged by 483.7%, highlighting the increasing sophistication of phishing tactics. The report also noted a 90.7% rise in cloud infrastructure abuse by attackers, reflecting a trend towards using trusted services in phishing schemes.

Why Early Detection is Crucial

The aftermath of a phishing attack can be severe, with stolen credentials potentially leading to account takeovers or unauthorized access to sensitive systems. For US organizations, campaigns targeting platforms like Microsoft 365 or using remote-management software pose significant risks, as evidenced by the CSuite campaign that primarily targeted US entities.

Early detection is vital for mitigating these risks. Identifying just one domain or URL linked to a phishing campaign can serve as a pivotal starting point for broader investigations into related infrastructure and potential threats.

Leveraging Threat Intelligence for Better Security

Threat intelligence offers SOCs and MSSPs a comprehensive view of the phishing landscape, enabling them to correlate suspicious activities with known malicious infrastructure. This intelligence is valuable across various stages of a phishing campaign, enhancing the ability to detect emerging threats before they impact users.

Interactive sandbox environments, like ANY.RUN’s, facilitate real-time analysis by allowing analysts to simulate phishing scenarios and observe network activities, providing insights beyond static URL or file assessments. This capability aids in faster decision-making and threat response.

Incorporating threat intelligence into existing security frameworks is not about replacing current systems but enhancing them. By integrating threat data with email alerts, DNS logs, and endpoint activities, SOCs and MSSPs can improve detection and response strategies, minimizing manual intervention and enabling more efficient operations.
Cyber Security News Tags:Attackers, Cybersecurity, Detection, Infrastructure, Malware, MSSPs, Phishing, Security, SOCs, threat intelligence

Post navigation

Previous Post: Preparing for Future Cyber Threats with Resilience
Next Post: Star Blizzard Hackers Target Organizations with Event Scams

Related Posts

PDFSIDER Malware Actively Used by Threat Actors to Bypass Antivirus and EDR Systems PDFSIDER Malware Actively Used by Threat Actors to Bypass Antivirus and EDR Systems Cyber Security News
Hackers Exploit Fake Government Sites for Unauthorized Access Hackers Exploit Fake Government Sites for Unauthorized Access Cyber Security News
Microsoft Domain Faces Trust Issues Due to Expired Certificate Microsoft Domain Faces Trust Issues Due to Expired Certificate Cyber Security News
Ransomware Disrupts BridgePay’s Nationwide Payment Processing Ransomware Disrupts BridgePay’s Nationwide Payment Processing Cyber Security News
New Report Uncover That Chinese Hackers Attempted To Compromise SentinelOne’s Own Servers New Report Uncover That Chinese Hackers Attempted To Compromise SentinelOne’s Own Servers Cyber Security News
Understanding OWASP Top 10 – Mitigating Web Application Vulnerabilities Understanding OWASP Top 10 – Mitigating Web Application Vulnerabilities Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • FAA Imposes Nationwide Ground Stop Amid Safety Concerns
  • US Halts $2.7 Billion in North Korean Crypto Theft
  • Hackers Exploit Fake Emails to Spread XLoader Malware
  • Trezor Addresses Security Risks in Compromised Wallets
  • SANSAR Malware Masks Cryptocurrency Mining on Linux Servers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • FAA Imposes Nationwide Ground Stop Amid Safety Concerns
  • US Halts $2.7 Billion in North Korean Crypto Theft
  • Hackers Exploit Fake Emails to Spread XLoader Malware
  • Trezor Addresses Security Risks in Compromised Wallets
  • SANSAR Malware Masks Cryptocurrency Mining on Linux Servers

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark