Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
InvisibleJS Emerges as Stealthy JavaScript Obfuscator Using Zero-Width Characters

InvisibleJS Emerges as Stealthy JavaScript Obfuscator Using Zero-Width Characters

Posted on January 12, 2026January 12, 2026 By CWS

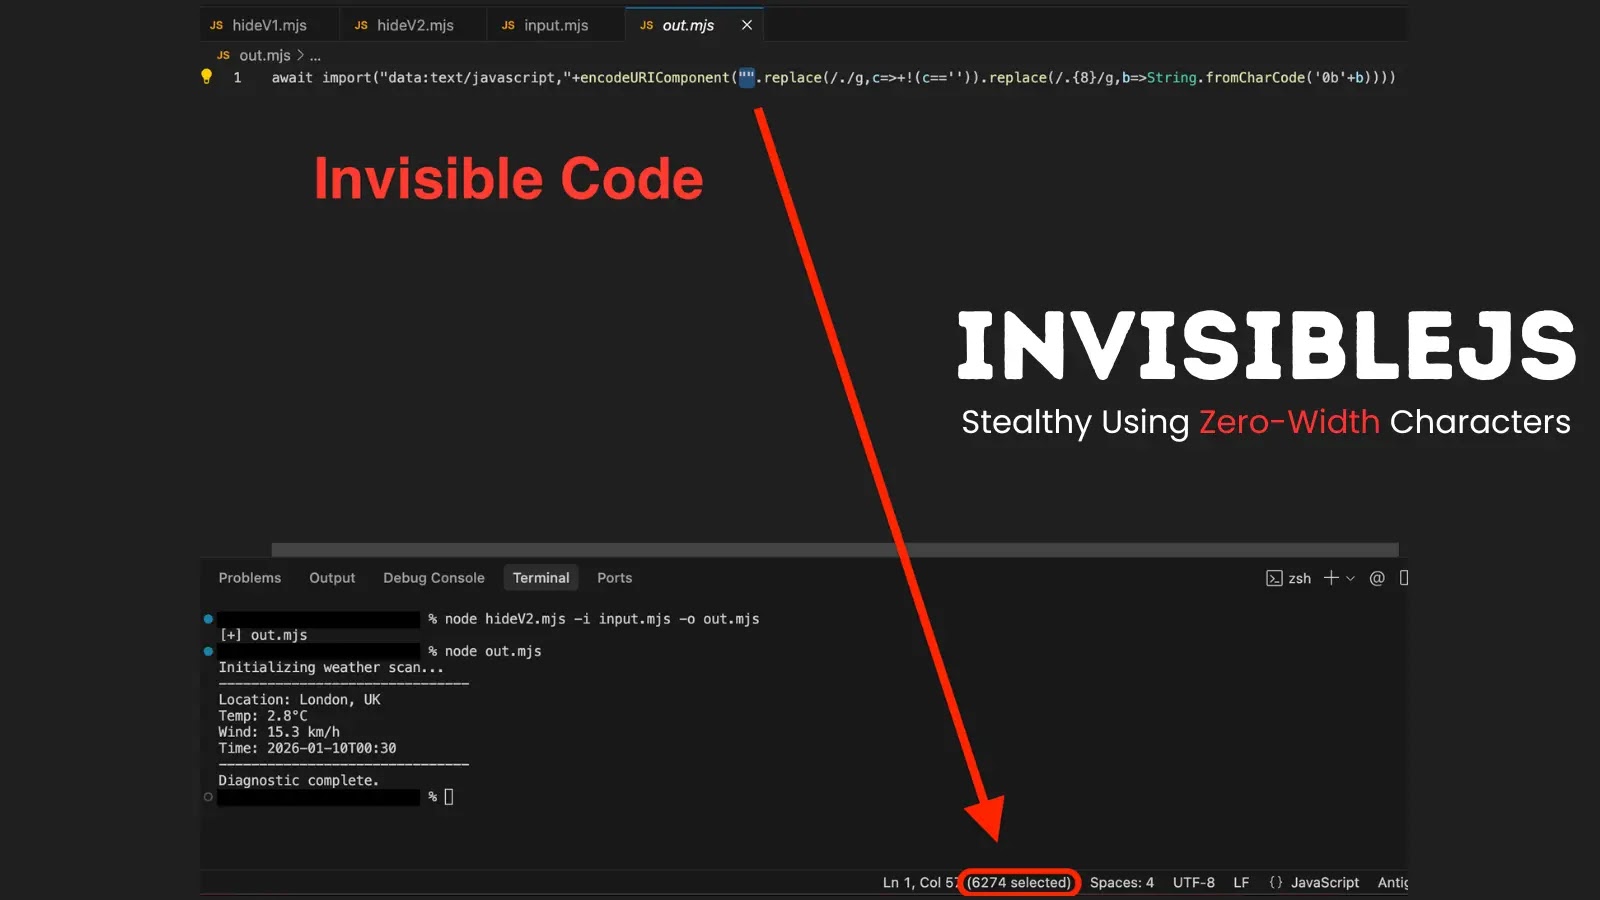
InvisibleJS, a brand new open-source software that conceals JavaScript code utilizing invisible zero-width Unicode characters, raises alarms about potential misuse in malware campaigns.

InvisibleJS, hosted on GitHub by developer With alias oscarmine, employs steganography to embed supply code into seemingly clean recordsdata. The method converts JavaScript into binary strings, mapping 0s to Zero Width House (U+200B) and 1s to Zero Width Non-Joiner (U+200C).

A small bootstrap loader then decodes and runs the hidden payload at runtime, making the code invisible to the bare eye in editors like VS Code.

Two Variations for Totally different Environments

The repository presents Model 1 (Traditional with eval), supreme for CommonJS and legacy Node.js setups, supporting require and module.exports natively.

Model 2 (Trendy with import) targets ES Modules, utilizing dynamic await import() for top-level await and exports, although it requires .mjs recordsdata or “sort”: module configuration.

Hiding code is easy by way of CLI:

Model 1: node hideV1.mjs -i enter.js -o hidden.js

Model 2: node hideV2.mjs -i enter.js -o hidden.js

Execution follows with node hidden.js, producing regular output regardless of the clean look.

FeatureVersion 1 (eval)Model 2 (import)Invisibility100percent100percentCommonJS SupportNativeLimitedESM SupportNoFullTop-Degree AwaitNoYesExecutionSynchronousAsynchronousDecoder LengthShortLong

This method echoes prior zero-width JS proofs-of-concept relationship again to 2018, now weaponized in phishing assaults. Attackers have abused related Unicode obfuscation utilizing Hangul characters for binary to cover payloads in scripts, evading scanners with anti-debug checks.

InvisibleJS might amplify such threats, enabling stealthy malware loaders in Node.js environments or net apps, complicating menace detection.

As obfuscation instruments proliferate, safety groups should improve Unicode-aware scanning and behavioral evaluation. Whereas pitched experimentally, InvisibleJS underscores the dual-use nature of coding improvements in cybersecurity.

Observe us on Google Information, LinkedIn, and X for day by day cybersecurity updates. Contact us to function your tales.
Cyber Security News Tags:Characters, Emerges, InvisibleJS, JavaScript, Obfuscator, Stealthy, ZeroWidth

Post navigation

Previous Post: Instagram Fixes Password Reset Vulnerability Amid User Data Leak
Next Post: Cyber Insights 2026: What CISOs Can Expect in 2026 and Beyond

Related Posts

New Charon Ransomware Employs DLL Sideloading, and Anti-EDR Capabilities to Attack Organizations New Charon Ransomware Employs DLL Sideloading, and Anti-EDR Capabilities to Attack Organizations Cyber Security News
New Ghost-tapping Attacks Steal Customers’ Cards Linked to Services Like Apple Pay and Google Pay New Ghost-tapping Attacks Steal Customers’ Cards Linked to Services Like Apple Pay and Google Pay Cyber Security News
PipeMagic Malware Mimic as ChatGPT App Exploits Windows Vulnerability to Deploy Ransomware PipeMagic Malware Mimic as ChatGPT App Exploits Windows Vulnerability to Deploy Ransomware Cyber Security News
Synology BeeStation 0-Day Vulnerability Let Remote Attackers Execute Arbitrary Code Synology BeeStation 0-Day Vulnerability Let Remote Attackers Execute Arbitrary Code Cyber Security News
Trivy GitHub Attack Exposes CI/CD Pipelines to Credential Theft Trivy GitHub Attack Exposes CI/CD Pipelines to Credential Theft Cyber Security News
CISA Alerts on Critical SharePoint Vulnerability CISA Alerts on Critical SharePoint Vulnerability Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Citrix Faces Critical NetScaler RCE Vulnerabilities
  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Citrix Faces Critical NetScaler RCE Vulnerabilities
  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark