Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
U.S. Agencies Alert on Siemens PLC Cyber Threats

U.S. Agencies Alert on Siemens PLC Cyber Threats

Posted on August 20, 2026 By CWS

Several U.S. federal agencies have issued a joint alert on August 19, highlighting active cyber threats against Siemens S7 Series programmable logic controllers (PLCs) within critical infrastructure sectors. This warning underscores the urgent need for enhanced cybersecurity measures across the nation.

Active Threats to Siemens PLCs

The advisory from the NSA, CISA, FBI, Department of Energy, and EPA describes the cyber risk as ongoing and significant. Hackers are reportedly using AI-generated scripts that mimic legitimate monitoring tools to infiltrate devices exposed to the Internet.

Attackers are leveraging Internet scanning platforms like Censys and ZoomEye to identify Siemens S7 PLCs that are either publicly accessible or poorly isolated from corporate networks. Post identification, they employ AI-assisted techniques to quickly create and modify exploitation code, making it easier to breach these industrial systems.

Methods and Tools Used in Attacks

The hacking tools utilize open-source automation libraries such as snap7.dll and python-snap7, enabling unauthorized read and write operations on PLC memory and configuration data via the S7comm protocol. These activities are disguised as normal monitoring operations, reducing the chances of detection.

All major Siemens S7 lines, including S7-200, S7-300, S7-400, S7-1200, and S7-1500, are at risk, along with the F-series safety controllers. Hackers are exploiting devices with default or weak credentials, facilitating easy access where security practices are lax.

Implications and Recommended Actions

Current activities suggest persistent reconnaissance and the development of exploit capabilities, rather than immediate sabotage. Hackers seem to be preparing for potential future attacks that could disrupt industrial operations.

Key sectors affected include Critical Manufacturing, Energy, Water and Wastewater, and more, with the Defense Industrial Base also identified as a possible target. Recent cyber incidents in U.S. water utilities highlight the ongoing threat to operational technology systems.

Potential impacts include disrupted processes, safety incidents, equipment damage, and extended downtimes. In response, agencies urge operators to conduct comprehensive inventories of their S7 devices, update firmware, and strengthen network security measures.

Specific actions include blocking TCP port 102, ensuring no PLC is directly internet-accessible, and tightening access controls. Continuous monitoring for anomalous traffic and unauthorized activities is also critical.

Organizations are encouraged to report any suspicious activity to CISA or the FBI’s Internet Crime Complaint Center. Adherence to these guidelines is crucial to safeguarding critical infrastructure from cyber threats.

Cyber Security News Tags:CISA, critical infrastructure, cyber threats, Cybersecurity, FBI, NSA, Siemens PLC

Post navigation

Previous Post: Elementor Pro Flaw Allows Remote Code Execution Risk
Next Post: AI-Driven Cyber Attacks Target Siemens PLCs in US

Related Posts

SCALR AI: A Free AI Platform for Security Teams SCALR AI: A Free AI Platform for Security Teams Cyber Security News
Critical Windows Active Directory Flaw Demands Immediate Action Critical Windows Active Directory Flaw Demands Immediate Action Cyber Security News
Microsoft August 2026 Security Patch Addresses Critical Vulnerabilities Microsoft August 2026 Security Patch Addresses Critical Vulnerabilities Cyber Security News
Darkhub: A Dark Web Hub for Cryptocurrency Fraud Darkhub: A Dark Web Hub for Cryptocurrency Fraud Cyber Security News
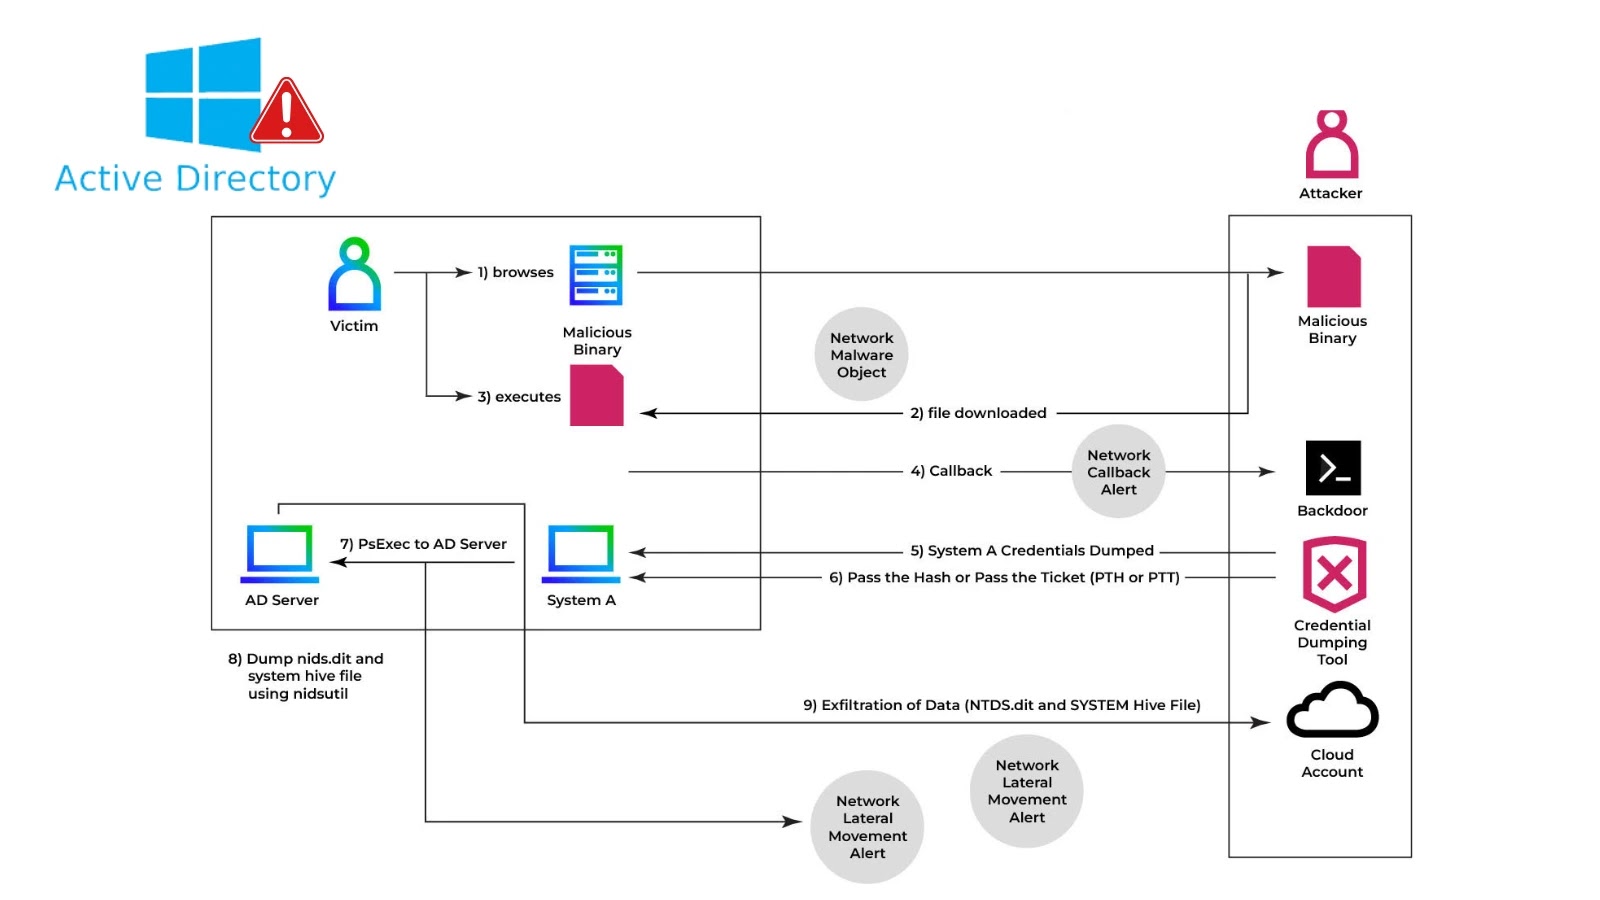
Hackers Compromise Active Directory to Steal NTDS.dit that Leads to Full Domain Compromise Hackers Compromise Active Directory to Steal NTDS.dit that Leads to Full Domain Compromise Cyber Security News
Threat Actors Leverage ChatGPT to Attack Mac Devices With AMOS InfoStealer Threat Actors Leverage ChatGPT to Attack Mac Devices With AMOS InfoStealer Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Trump Appoints Clayton to Lead Federal AI Task Force
  • South Korea Initiates Security Overhaul After Bank Data Breaches
  • China-Linked TA419 Targets U.S. AI Experts with Phishing
  • Key Arrest in ShinyHunters Case Aids FBI Investigation
  • Vercel Unveils KVM Zero-Day Flaw, Rewards Researcher $50K

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Trump Appoints Clayton to Lead Federal AI Task Force
  • South Korea Initiates Security Overhaul After Bank Data Breaches
  • China-Linked TA419 Targets U.S. AI Experts with Phishing
  • Key Arrest in ShinyHunters Case Aids FBI Investigation
  • Vercel Unveils KVM Zero-Day Flaw, Rewards Researcher $50K

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark