Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
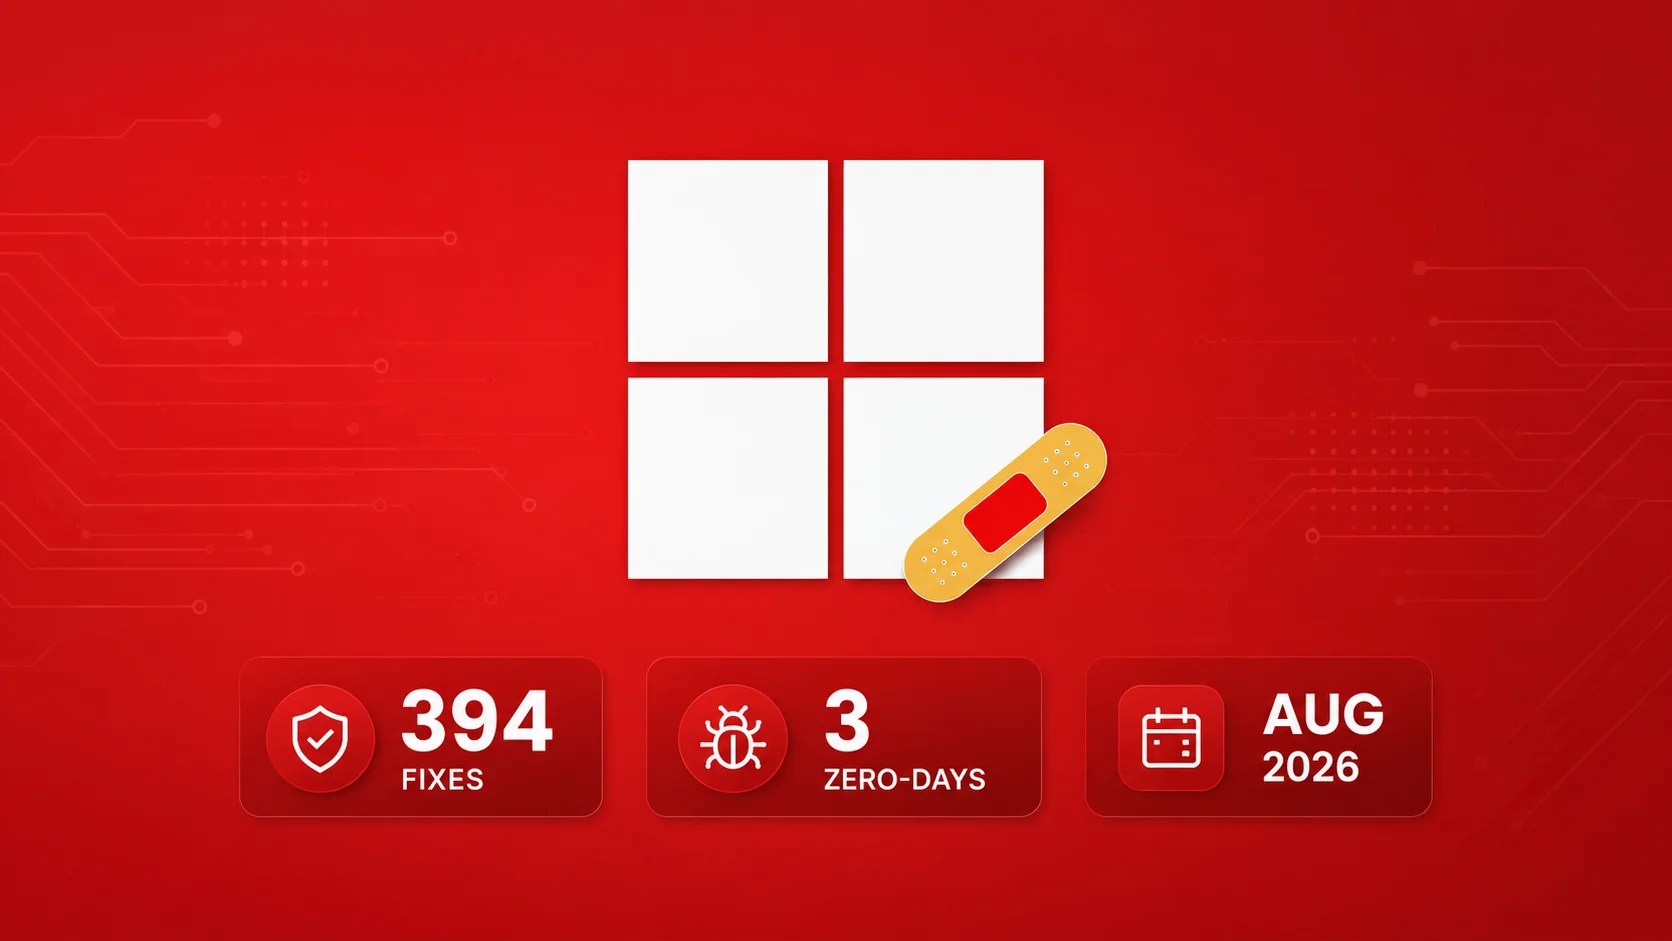
Microsoft August 2026 Security Patch Addresses Critical Vulnerabilities

Microsoft August 2026 Security Patch Addresses Critical Vulnerabilities

Posted on August 11, 2026 By CWS

Microsoft has released its August 2026 security update, aiming to address multiple critical vulnerabilities across its product suite. This monthly Patch Tuesday rollout is crucial for maintaining system security and mitigating potential threats.

Critical Vulnerabilities Highlighted

The update addresses several critical vulnerabilities, including remote code execution (RCE) flaws in Microsoft Office applications, such as Word and Excel. These RCE vulnerabilities represent significant security risks, potentially allowing attackers to execute arbitrary code on vulnerable systems. Microsoft has labeled several of these vulnerabilities as critical, underscoring the importance of applying the patches immediately.

Additionally, the update includes fixes for elevation of privilege vulnerabilities in Windows components like the Win32k kernel and various Windows services. Such vulnerabilities could be exploited by attackers to gain higher privileges on compromised systems, further emphasizing the necessity for timely updates.

Focus on Information Disclosure and Denial of Service

Information disclosure vulnerabilities were also targeted in this update, affecting products such as Microsoft SharePoint Server and Azure CycleCloud. These vulnerabilities could result in unauthorized access to sensitive information, posing a risk to data privacy and integrity.

Denial of Service (DoS) vulnerabilities were also addressed, with patches for Windows Management Services and the Windows Network File System. These vulnerabilities could allow attackers to disrupt service availability, thereby hampering business operations.

Recommendations for IT Administrators

IT administrators are strongly advised to prioritize the deployment of these updates across their networks. Ensuring all systems are up to date is critical to safeguarding against these newly disclosed vulnerabilities. Administrators should also review Microsoft’s detailed release notes to understand the specific impacts and guidance related to each vulnerability.

In conclusion, Microsoft’s August 2026 security patch is a vital update that addresses significant security threats. Organizations must act swiftly to implement these patches to protect their infrastructure from potential exploits.

Cyber Security News Tags:critical update, Cybersecurity, elevation of privilege, information disclosure, Microsoft, Patch Tuesday, remote code execution, security update, Vulnerabilities, Windows

Post navigation

Previous Post: Senate Bill Strengthens Cybersecurity for US Water Systems
Next Post: Microsoft Addresses Active Windows Zero-Day Vulnerability

Related Posts

Fake Bahrain App Exploits Android RAT for Data Theft Fake Bahrain App Exploits Android RAT for Data Theft Cyber Security News
Enhancing MSSP Security with Real-Time Threat Visibility Enhancing MSSP Security with Real-Time Threat Visibility Cyber Security News
Microsoft to Disable Inline SVG Images Display to Outlook for Web and Windows Users Microsoft to Disable Inline SVG Images Display to Outlook for Web and Windows Users Cyber Security News
Google Ad Used to Spread macOS Credential-Stealing Malware Google Ad Used to Spread macOS Credential-Stealing Malware Cyber Security News
Hackers Exploit AiTM to Misdirect Employee Salaries Hackers Exploit AiTM to Misdirect Employee Salaries Cyber Security News
Tego AI Exposes Potential Risks in Claude Tag Integration Tego AI Exposes Potential Risks in Claude Tag Integration Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark