Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
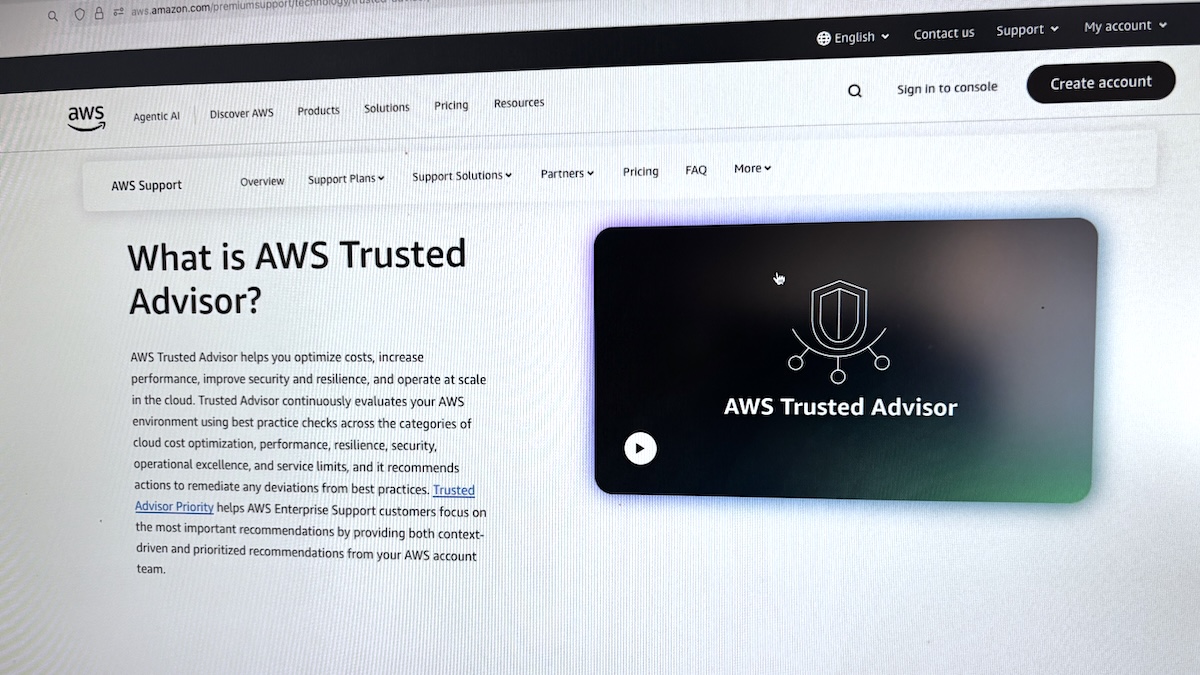
AWS Trusted Advisor Tricked Into Showing Unprotected S3 Buckets as Secure

AWS Trusted Advisor Tricked Into Showing Unprotected S3 Buckets as Secure

Posted on August 22, 2025August 22, 2025 By CWS

AWS has addressed a weak spot that might have been leveraged by attackers to forestall AWS Trusted Advisor from flagging unprotected S3 buckets as a threat.

AWS Trusted Advisor is designed to investigate clients’ environments and supply suggestions for enhancements in areas resembling price, efficiency, and safety. A number of security-related Trusted Advisor checks are supplied without cost, together with safety group settings, IAM person entry, multi-factor authentication, and S3 bucket permissions.

The S3 bucket permissions verify alerts customers when their buckets have open entry permissions or enable entry to any authenticated AWS person. 

Researchers at Fog Safety found that an attacker may get Trusted Advisor to not alert customers about public buckets by setting the S3 bucket insurance policies to disclaim ‘s3:GetBucketAcl’, ‘s3:GetPublicAccessBlock’ or ‘s3:GetBucketPolicyStatus’ actions. 

After bypassing Trusted Advisor’s S3 safety verify, the researchers confirmed how an attacker may have configured a bucket with public and nameless permissions through bucket insurance policies and ACLs, enabling knowledge exfiltration with out triggering an alert. 

It’s price noting that an attacker would want to first acquire entry to the goal’s AWS atmosphere earlier than finishing up these actions. 

Fog Safety reported its findings to AWS in early Might and a complete repair was rolled out in late June — an incomplete patch was deployed in late Might. 

AWS has notified clients concerning the concern and pointed them to documentation pages overlaying S3 bucket permissions and blocking public entry to S3 storage. Commercial. Scroll to proceed studying.

“As a safety finest follow, we suggest clients overview their S3 bucket permissions and guarantee they align with their safety necessities,” an AWS spokesperson advised SecurityWeek. “When S3 bucket insurance policies forestall Trusted Advisor from performing sure actions […], clients ought to anticipate to see a ‘Warn’ standing of their Trusted Advisor verify. Beforehand, these buckets had been incorrectly listed as ignored and probably displayed incorrect standing indicators for public entry settings.”

Associated: Distributors Unveil New Cloud Safety Merchandise, Options at AWS re:Invent 2024

Associated: Compromised AWS Keys Abused in Codefinger Ransomware Assaults

Associated: Vulnerability Allowed Takeover of AWS Apache Airflow Service

Security Week News Tags:Advisor, AWS, Buckets, Secure, Showing, Tricked, Trusted, Unprotected

Post navigation

Previous Post: Microsoft Warns of Hackers Using ClickFix Technique to Attack Windows and macOS Devices
Next Post: CPAP Medical Data Breach Impacts 90,000 People

Related Posts

Stolen Credentials: A Persistent Threat to Cybersecurity Stolen Credentials: A Persistent Threat to Cybersecurity Security Week News
AIUC Secures M to Enhance AI Agent Certification AIUC Secures $40M to Enhance AI Agent Certification Security Week News
Cybereason Acquired by MSSP Giant LevelBlue Cybereason Acquired by MSSP Giant LevelBlue Security Week News
AIUC Secures M to Enhance AI Agent Certification NewCore Launches with $66 Million in Seed Funding Security Week News
Mate Emerges From Stealth Mode With .5 Million in Seed Funding Mate Emerges From Stealth Mode With $15.5 Million in Seed Funding Security Week News
Ryan Davis: Transition from Hacker to CISO at New Charter Ryan Davis: Transition from Hacker to CISO at New Charter Security Week News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity
  • SGLang Exploit Breach Exposes NEAR AI User Data
  • Ivanti Releases Critical Security Updates for Key Products
  • Microsoft’s November Patch Tuesday Fixes 1,094 Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • Microsoft Addresses 1,093 Vulnerabilities in November 2026 Patch
  • WhiteMatter Secures $20M Series A for AI Cybersecurity
  • SGLang Exploit Breach Exposes NEAR AI User Data
  • Ivanti Releases Critical Security Updates for Key Products
  • Microsoft’s November Patch Tuesday Fixes 1,094 Vulnerabilities

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark