Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Malicious Chrome Extension as Ethereum Wallet Enables Full Wallet Takeover

Malicious Chrome Extension as Ethereum Wallet Enables Full Wallet Takeover

Posted on November 14, 2025November 14, 2025 By CWS

A misleading Chrome extension named Safery: Ethereum Pockets has emerged as a critical menace to cryptocurrency customers.

Revealed on the Chrome Internet Retailer on November 12, 2024, this extension masquerades as a safe Ethereum pockets whereas secretly stealing person seed phrases.

The malware’s refined design permits attackers to realize full management over victims’ cryptocurrency wallets and drain their digital belongings.

The extension operates with a crafty strategy to theft. When customers create or import a pockets, the extension extracts their seed phrase and encodes it into artificial Sui blockchain addresses.

It then broadcasts tiny microtransactions of 0.000001 SUI to those encoded addresses from a menace actor-controlled pockets. To observers, these seem as regular blockchain exercise, however they really comprise hidden person information.

Socket.dev safety analysts recognized the malicious extension and found its evasive techniques.

The researchers famous that the backdoor makes use of BIP-39 mnemonic encoding, remodeling every seed phrase phrase into numeric indices and packing them into hexadecimal strings that resemble reputable Sui pockets addresses.

Ethereum Pockets markets the extension as a easy, safe ETH pockets (Supply – Socket.dev)

This intelligent strategy hides information inside blockchain transactions, eliminating the necessity for conventional command-and-control servers.

Technical Mechanism

The technical mechanism reveals the extension’s sophistication. When analyzing the extension code, analysts discovered it masses an ordinary wordlist, maps every phrase to its index, and constructs artificial addresses prefixed with “0x”.

A paired decoder embedded within the malware permits the menace actor to reverse this course of, reconstructing the unique seed phrase phrase by phrase.

The code silently executes these operations after a person enters their seed phrase, sending exfiltration information throughout the blockchain earlier than finishing the login course of.

The menace proves particularly harmful as a result of the extension seems reputable on the Chrome Internet Retailer. Customers looking for Ethereum wallets discover it listed because the fourth outcome alongside trusted options like MetaMask and Enkrypt, lending it false credibility.

As soon as a sufferer installs the extension and imports their pockets, the attacker beneficial properties entry to all derived Ethereum personal keys and might switch all belongings to their very own addresses, leading to full monetary compromise.

Comply with us on Google Information, LinkedIn, and X to Get Extra Immediate Updates, Set CSN as a Most well-liked Supply in Google.

Cyber Security News Tags:Chrome, Enables, Ethereum, Extension, Full, Malicious, Takeover, Wallet

Post navigation

Previous Post: Now-Patched Fortinet FortiWeb Flaw Exploited in Attacks to Create Admin Accounts
Next Post: Critical Imunify360 AV Vulnerability Exposes 56 Million Linux-hosted Websites to RCE Attacks

Related Posts

Critical Linux Flaw Allows KVM Escape with Root Access Critical Linux Flaw Allows KVM Escape with Root Access Cyber Security News
Hackers Exploit AI Tools for Advanced Cyber Attacks Hackers Exploit AI Tools for Advanced Cyber Attacks Cyber Security News
BreachLock Expands AEV to Web Applications BreachLock Expands AEV to Web Applications Cyber Security News
CISA Warns of Android 0-Day Use-After-Free Vulnerability Exploited in Attacks CISA Warns of Android 0-Day Use-After-Free Vulnerability Exploited in Attacks Cyber Security News
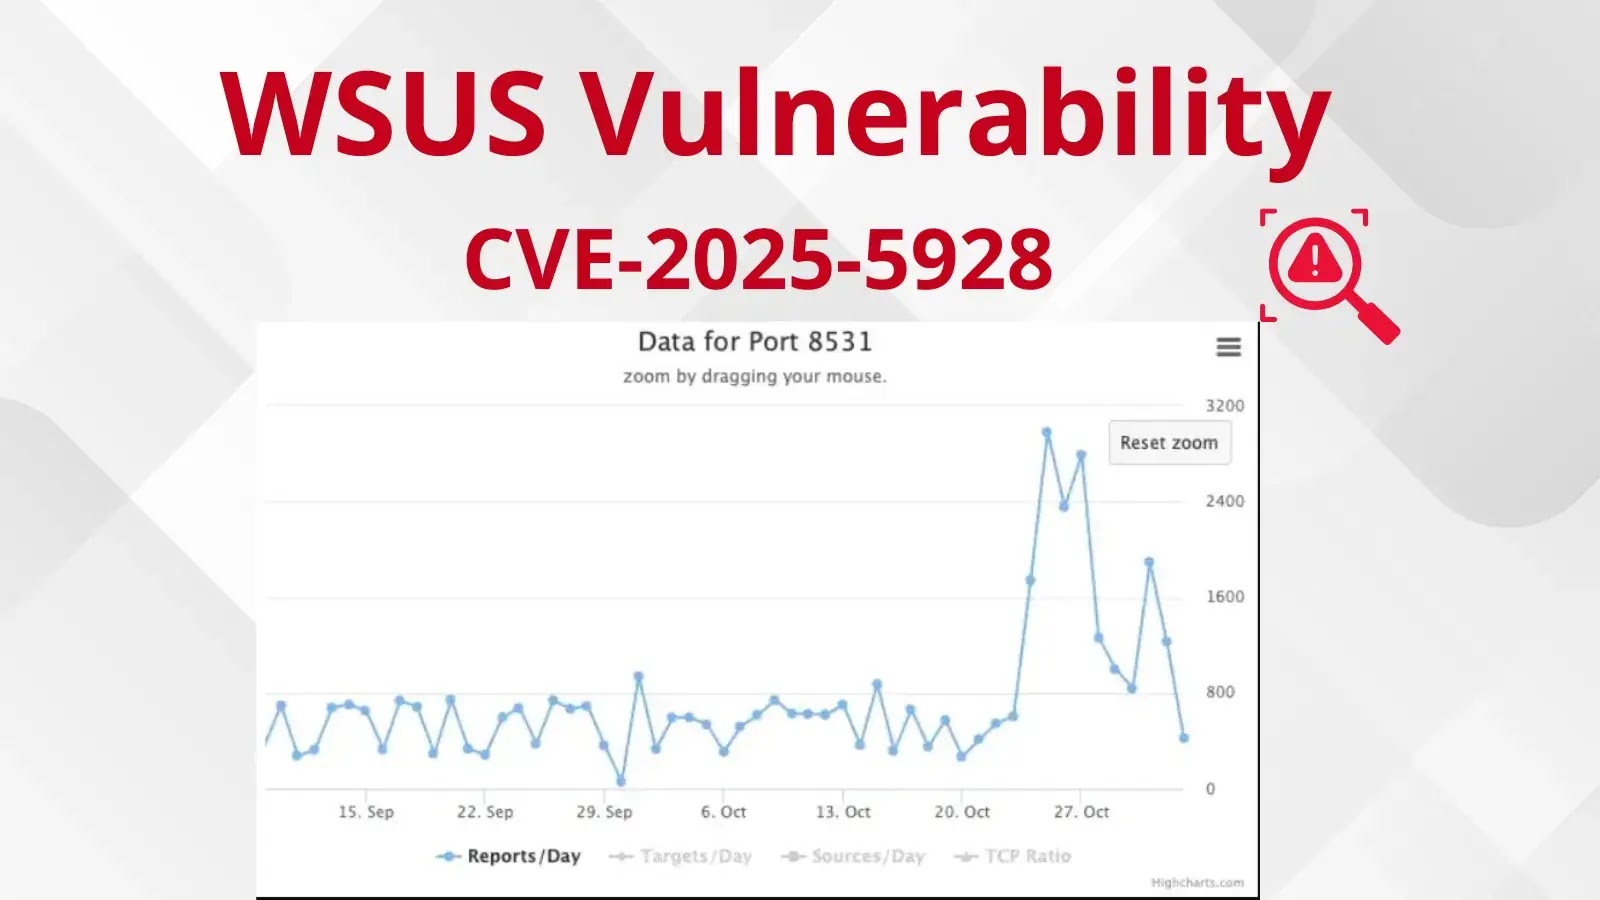
Hackers Actively Scanning for TCP Port 8530/8531 Linked to WSUS Vulnerability CVE-2025-59287 Hackers Actively Scanning for TCP Port 8530/8531 Linked to WSUS Vulnerability CVE-2025-59287 Cyber Security News
New Malware Toolkit Sends Users to Malicious Websites While the URL Stays the Same New Malware Toolkit Sends Users to Malicious Websites While the URL Stays the Same Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark