Skip to content
  • Home
  • Cyber Map
  • About Us – Contact
  • Disclaimer
  • Terms and Rules
  • Privacy Policy
Cyber Web Spider Blog – News

Cyber Web Spider Blog – News

Globe Threat Map provides a real-time, interactive 3D visualization of global cyber threats. Monitor DDoS attacks, malware, and hacking attempts with geo-located arcs on a rotating globe. Stay informed with live logs and archive stats.

  • Home
  • Cyber Map
  • Cyber Security News
  • Security Week News
  • The Hacker News
  • How To?
  • Toggle search form
Salty2FA and Tycoon2FA Phishing Kits Attacking Enterprise Users to Steal Login Credentials

Salty2FA and Tycoon2FA Phishing Kits Attacking Enterprise Users to Steal Login Credentials

Posted on December 2, 2025December 2, 2025 By CWS

A brand new kind of phishing assault that mixes two totally different phishing kits: Salty2FA and Tycoon2FA. This marks a major change within the Phishing-as-a-Service (PhaaS) panorama.

Whereas phishing kits sometimes preserve distinctive signatures of their code and supply mechanisms, latest campaigns concentrating on enterprise customers have begun deploying payloads that mix parts from each frameworks.

This convergence complicates attribution efforts and suggests a possible operational merger or collaboration between the menace actors behind these subtle instruments.​

The Collapse of Salty2FA

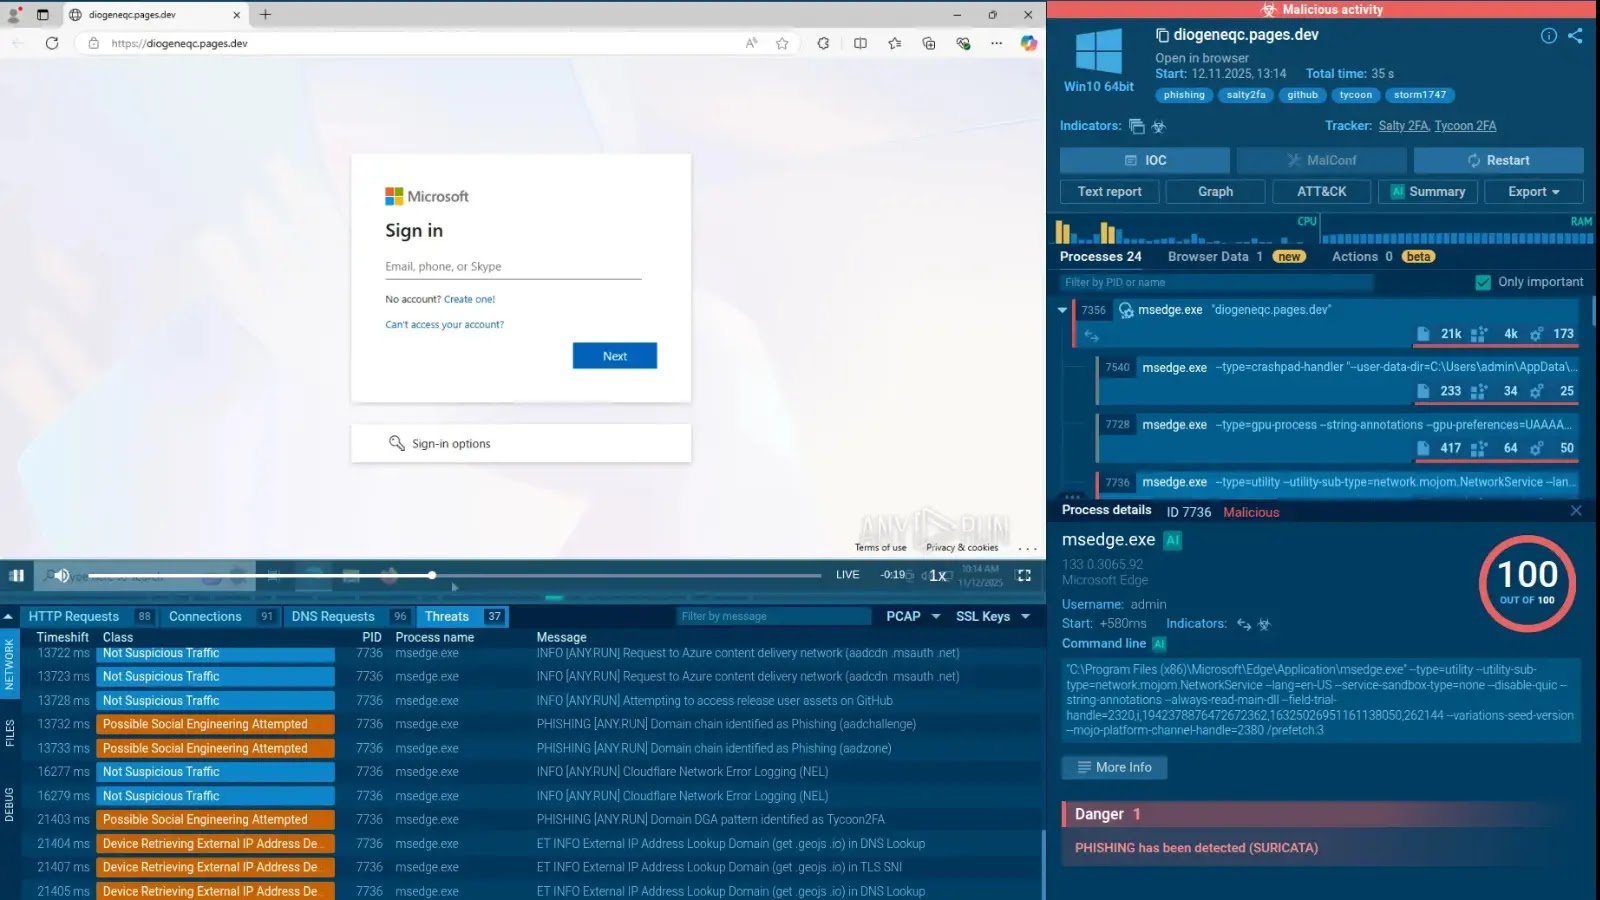
The invention follows a dramatic decline in standalone Salty2FA exercise noticed in late 2025, in keeping with an evaluation by ANY.RUN, submissions of Salty2FA samples to their interactive sandbox dropped precipitously from lots of of weekly uploads to fewer than 50 by early November.

Coinciding with this drop, analysts detected a wave of “hybrid” samples the place Salty2FA’s infrastructure appeared to fail, triggering a fallback mechanism that retrieved Tycoon2FA payloads as a substitute.​

Code-level evaluation by ANY.RUN revealed that these hybrid payloads start with Salty2FA’s conventional “trampoline” scripts, which load the following stage of the assault.

Nonetheless, when the first Salty2FA domains didn’t resolve (returning DNS SERVFAIL errors), the scripts executed a hardcoded fallback command, fetching malicious content material from Tycoon2FA infrastructure.

This seamless handoff signifies that the operators anticipated infrastructure instability and engineered a redundancy utilizing a rival or accomplice equipment.​

The overlap in techniques, methods, and procedures (TTPs) strengthens the speculation that each kits could also be operated by the identical menace group, tracked by Microsoft as Storm-1747.

Storm-1747 has lengthy been related to Tycoon2FA, a equipment recognized for bypassing multifactor authentication (MFA) by way of adversary-in-the-middle (AiTM) methods.​

The newly noticed hybrid samples replicate Tycoon2FA’s execution chain virtually line-for-line of their later levels, together with particular variable naming conventions and knowledge encryption strategies.

This structural similarity means that Salty2FA might not be an impartial competitor however relatively one other software in Storm-1747’s arsenal, probably used for various concentrating on profiles or as a testing floor for brand spanking new evasion options.​

For safety operations facilities (SOCs), the blurring of strains between Salty2FA and Tycoon2FA requires an up to date protection technique. Reliance on static indicators of compromise (IOCs) for a single equipment is not ample, as a marketing campaign may pivot from one framework to a different mid-execution.​

Specialists advocate treating these kits as a single menace cluster. Defenders ought to correlate alerts involving Salty2FA’s preliminary supply vectors, reminiscent of HTML trampoline recordsdata, with Tycoon2FA’s recognized community behaviors, together with visitors to DGA-generated domains and fast-flux infrastructure.

By unifying detection logic for each households, organizations can higher detect these resilient, multi-stage assaults earlier than credentials are stolen.

​Detect phishing threats in below 60 seconds with ANY.RUN’s Sandbox in your SOC => Join now
Cyber Security News Tags:Attacking, Credentials, Enterprise, Kits, Login, Phishing, Salty2FA, Steal, Tycoon2FA, Users

Post navigation

Previous Post: Water Saci Hackers Leveraging AI Tools to Attack WhatsApp Web Users
Next Post: Hackers Leverage Evilginx to Undermine MFA Security Mimicking Legitimate SSO Sites

Related Posts

Windows Agere Modem Driver 0-Day Vulnerabilities Actively Exploited To Escalate Privileges Windows Agere Modem Driver 0-Day Vulnerabilities Actively Exploited To Escalate Privileges Cyber Security News
Linux Kernel Bridge Vulnerability Exposes Security Risks Linux Kernel Bridge Vulnerability Exposes Security Risks Cyber Security News
New Supply Chain Attack Targets Legitimate npm Package with 45,000 Weekly Downloads New Supply Chain Attack Targets Legitimate npm Package with 45,000 Weekly Downloads Cyber Security News
25,000+ FortiCloud SSO-Enabled Devices Exposed to Remote Attacks 25,000+ FortiCloud SSO-Enabled Devices Exposed to Remote Attacks Cyber Security News
Microsoft 365 Introduces Copilot Cowork for Task Automation Microsoft 365 Introduces Copilot Cowork for Task Automation Cyber Security News
CISA Warns of Rails Ruby on Rails Path Traversal Vulnerability Exploited in Attacks CISA Warns of Rails Ruby on Rails Path Traversal Vulnerability Exploited in Attacks Cyber Security News

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025

Recent Posts

  • F-Droid 2.0 Debuts with Major Redesign for App Discovery
  • China and US to Create AI Safety Channel Amid Ongoing Talks
  • Lunex Stealer Exploits AMD Driver for Credential Theft
  • Local AI Model Evades EDR Detection with Modified Credential Dumper
  • Enhancing AI Agent Security with Zero Trust Principles

Pages

  • About Us – Contact
  • Disclaimer
  • Privacy Policy
  • Terms and Rules

Categories

  • Cyber Security News
  • How To?
  • Security Week News
  • The Hacker News

Copyright © 2026 Cyber Web Spider Blog – News.

Powered by PressBook Masonry Dark